proomt

Search

Search posts, papers, and topics

All posts

Freek Van der Herten1 min readintro
Flare now uses OAuth for MCP, the CLI, and API

Summary

Flare has replaced its legacy token‑based authentication with OAuth for its MCP clients, CLI, and API, introducing scoped permissions and a unified management UI. The change simplifies setup and enables fine‑grained read‑only or project‑level access.

  • Flare switched from long‑lived tokens to OAuth for MCP, CLI, and API access.
  • OAuth scopes provide read‑only and project‑level permissions.
  • Setup is faster because credentials are managed centrally.
  • All connections are now managed from a single place in the Flare UI.

Anyone integrating with Flare needs to update their authentication flow to use OAuth and can now enforce tighter permission boundaries.

4/10
Related reading

  1. Why we removed AI solutions from Flare

    Flare dropped its AI‑generated solution feature, saying it no longer matches how developers debug with modern coding agents. The new approach uses an MCP server, a CLI, a "Copy" tool for prompts, and docs tuned for agents, but the post gives no technical details or data.

    Freek Van der Hertenfreek.dev1 min
  2. WebMCP support now available in mcp-handler

    Vercel's mcp-handler 2.2.0 adds experimental WebMCP support, letting you expose registered MCP tools to in‑browser agents via a single script tag. The script proxies tool calls back to your MCP server with the signed‑in user’s credentials, so no extra OAuth flow is needed.

    Vercelvercel.com1 minrelease
  3. Laravel MCP 1.0 Is Released

    Laravel MCP 1.0 ships with the 2026-07-28 protocol, adding searchable tool catalogs, cache hints, stateless request handling, and PKCE‑required OAuth with client‑metadata support. The release includes migration guidance and new headers for versioned RPC calls.

    Laravellaravel-news.com3 minrelease
  4. Optimize Your Identity Flows with Auth0 Identity Conversion Suite

    Auth0 announced the early‑access Identity Conversion Suite, which adds two features—Anonymous Sessions (tracking a user before they log in via OAuth‑compatible tokens) and Experiment Center (feature‑flag‑driven A/B testing of auth flows). The post explains the intended use cases (guest checkout, secure anonymous API access, passwordless sign‑up, MFA sizing) but provides no implementation details,…

    Auth0auth0.com7 min
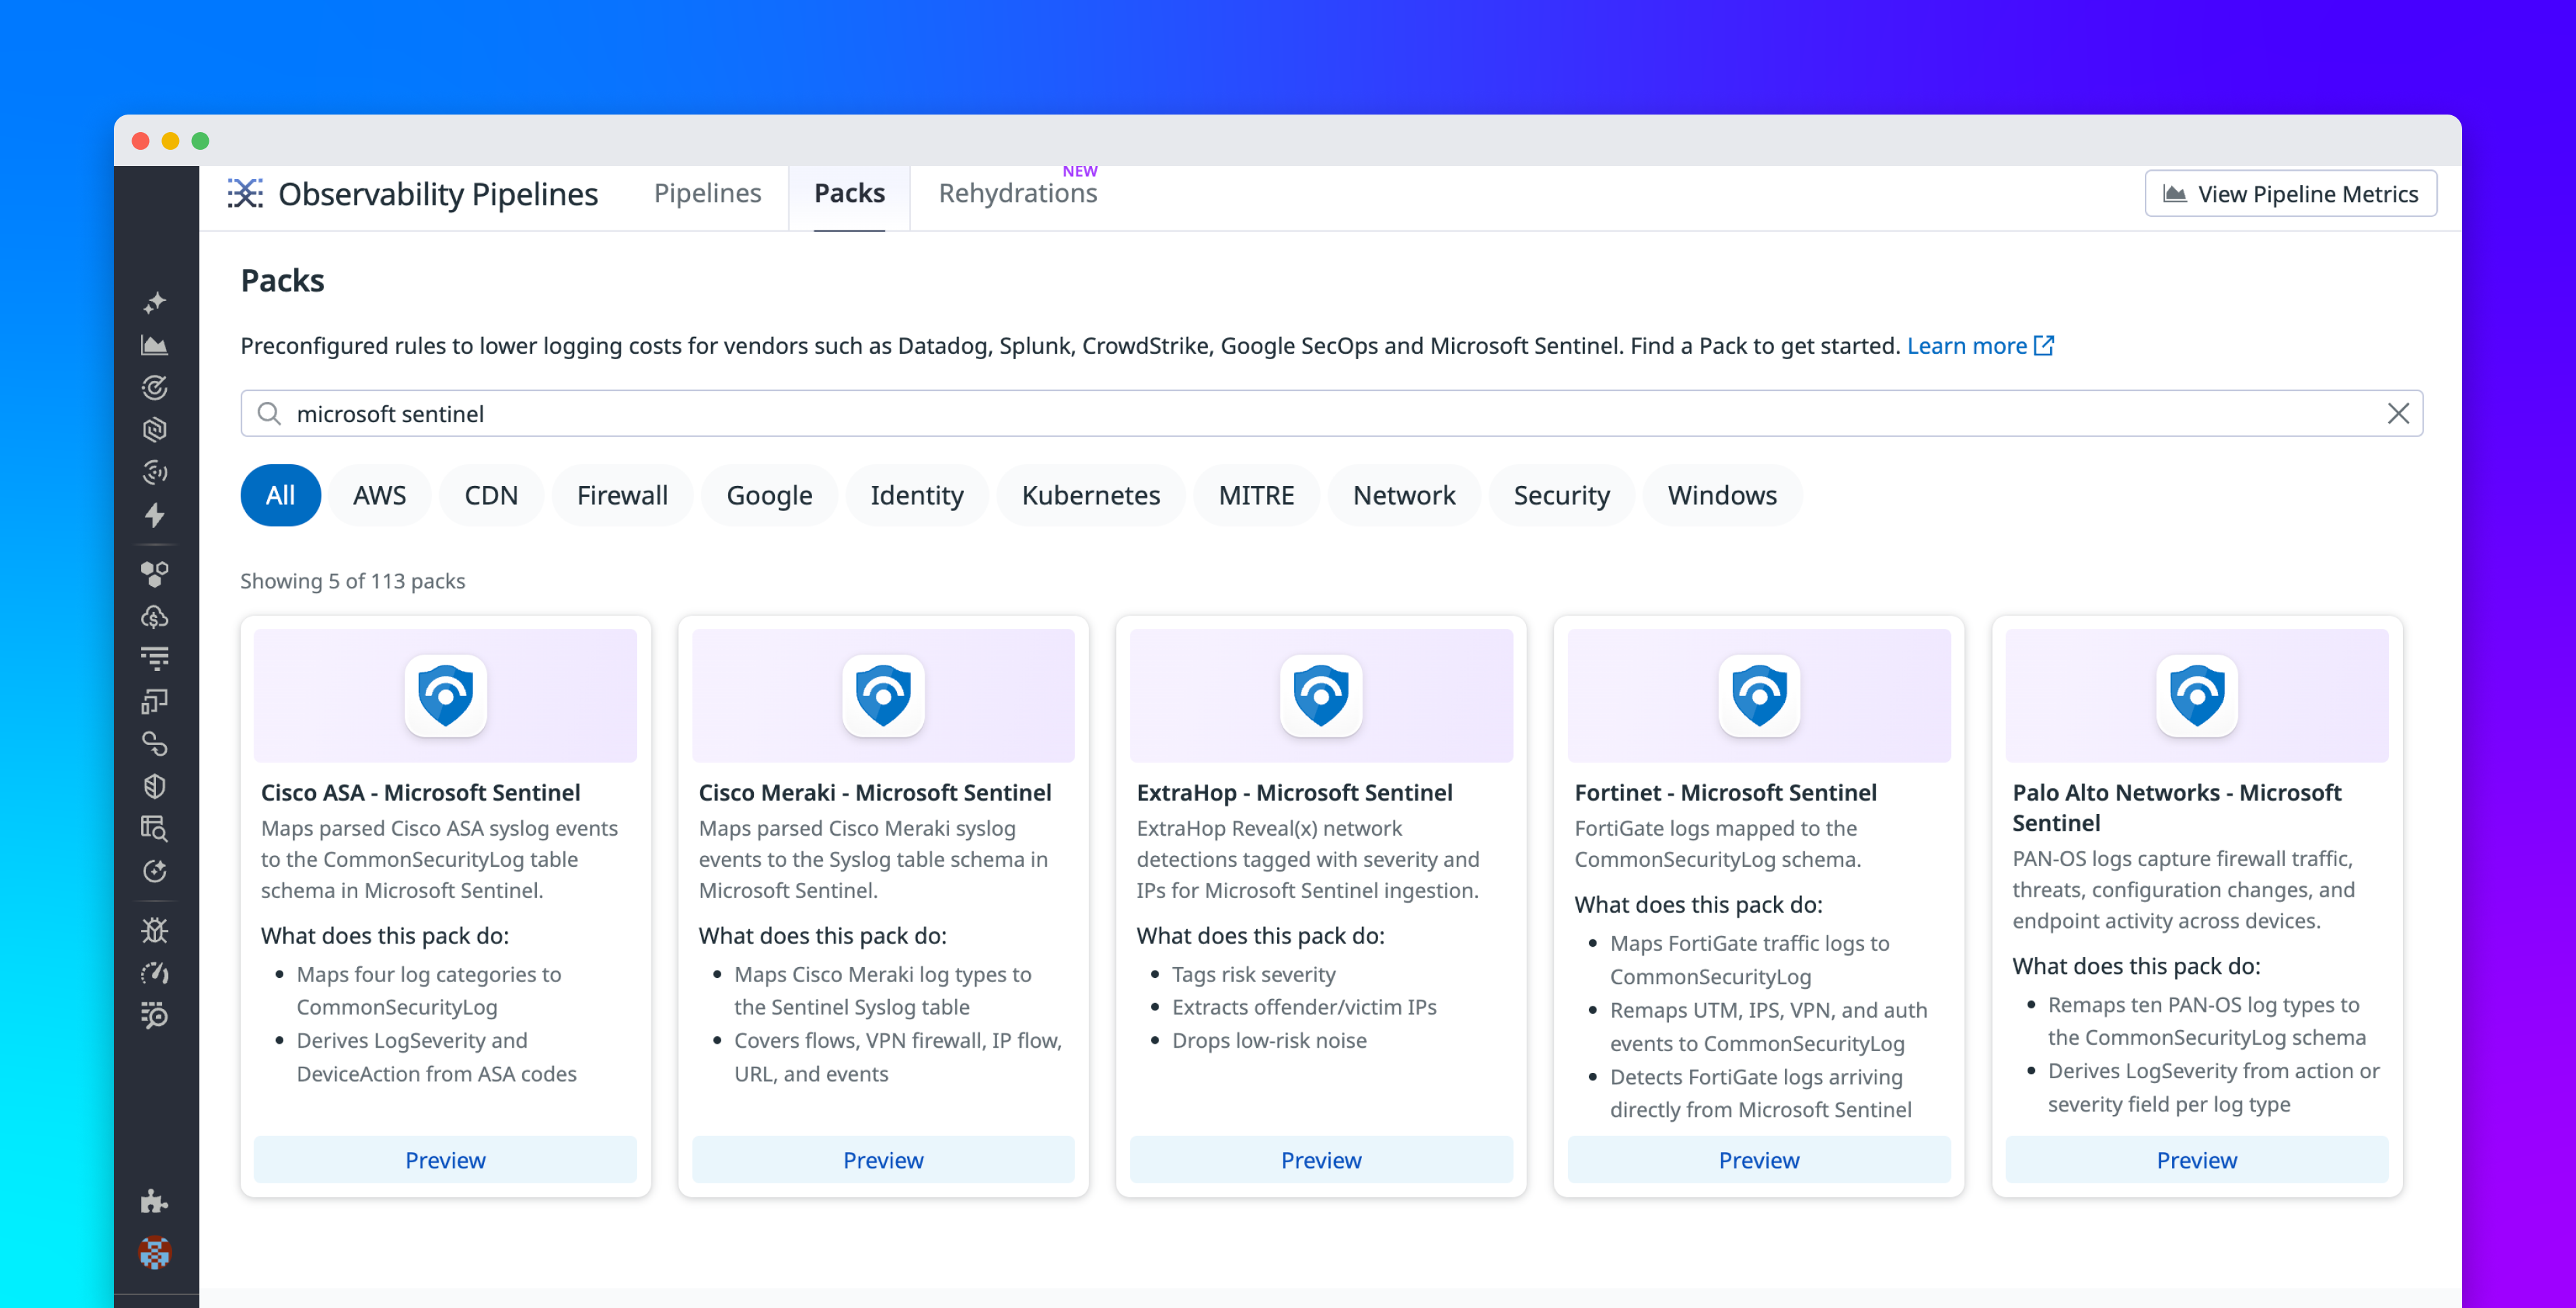
  5. Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

    Datadog Observability Pipelines now ships pre‑built Microsoft Sentinel Packs that map logs from Palo Alto, Fortinet, Cisco ASA, Cisco Meraki, and ExtraHop into Sentinel’s CommonSecurityLog or Syslog tables. Packs handle field extraction, severity derivation, and device‑action mapping, letting you filter or drop low‑value events before ingest, validate mappings with Live Capture, and reduce per‑GB…

    Datadogdatadoghq.com5 min
  6. Introducing: Dark mode for Flare

    Flare adds a dark theme. The post outlines the design steps: defining semantic color tokens, adjusting gradients and shadows, and using side‑by‑side screenshots to verify the light theme stays unchanged. Accessibility is mentioned but no code or measurable results are provided.

    Freek Van der Hertenfreek.dev1 min