proomt

Search

Search posts, papers, and topics

All posts

LaravelYannick Lyn Fatt3 min readintermediate
Difflock: Lint Laravel Migrations and Diff Your Schema

Summary

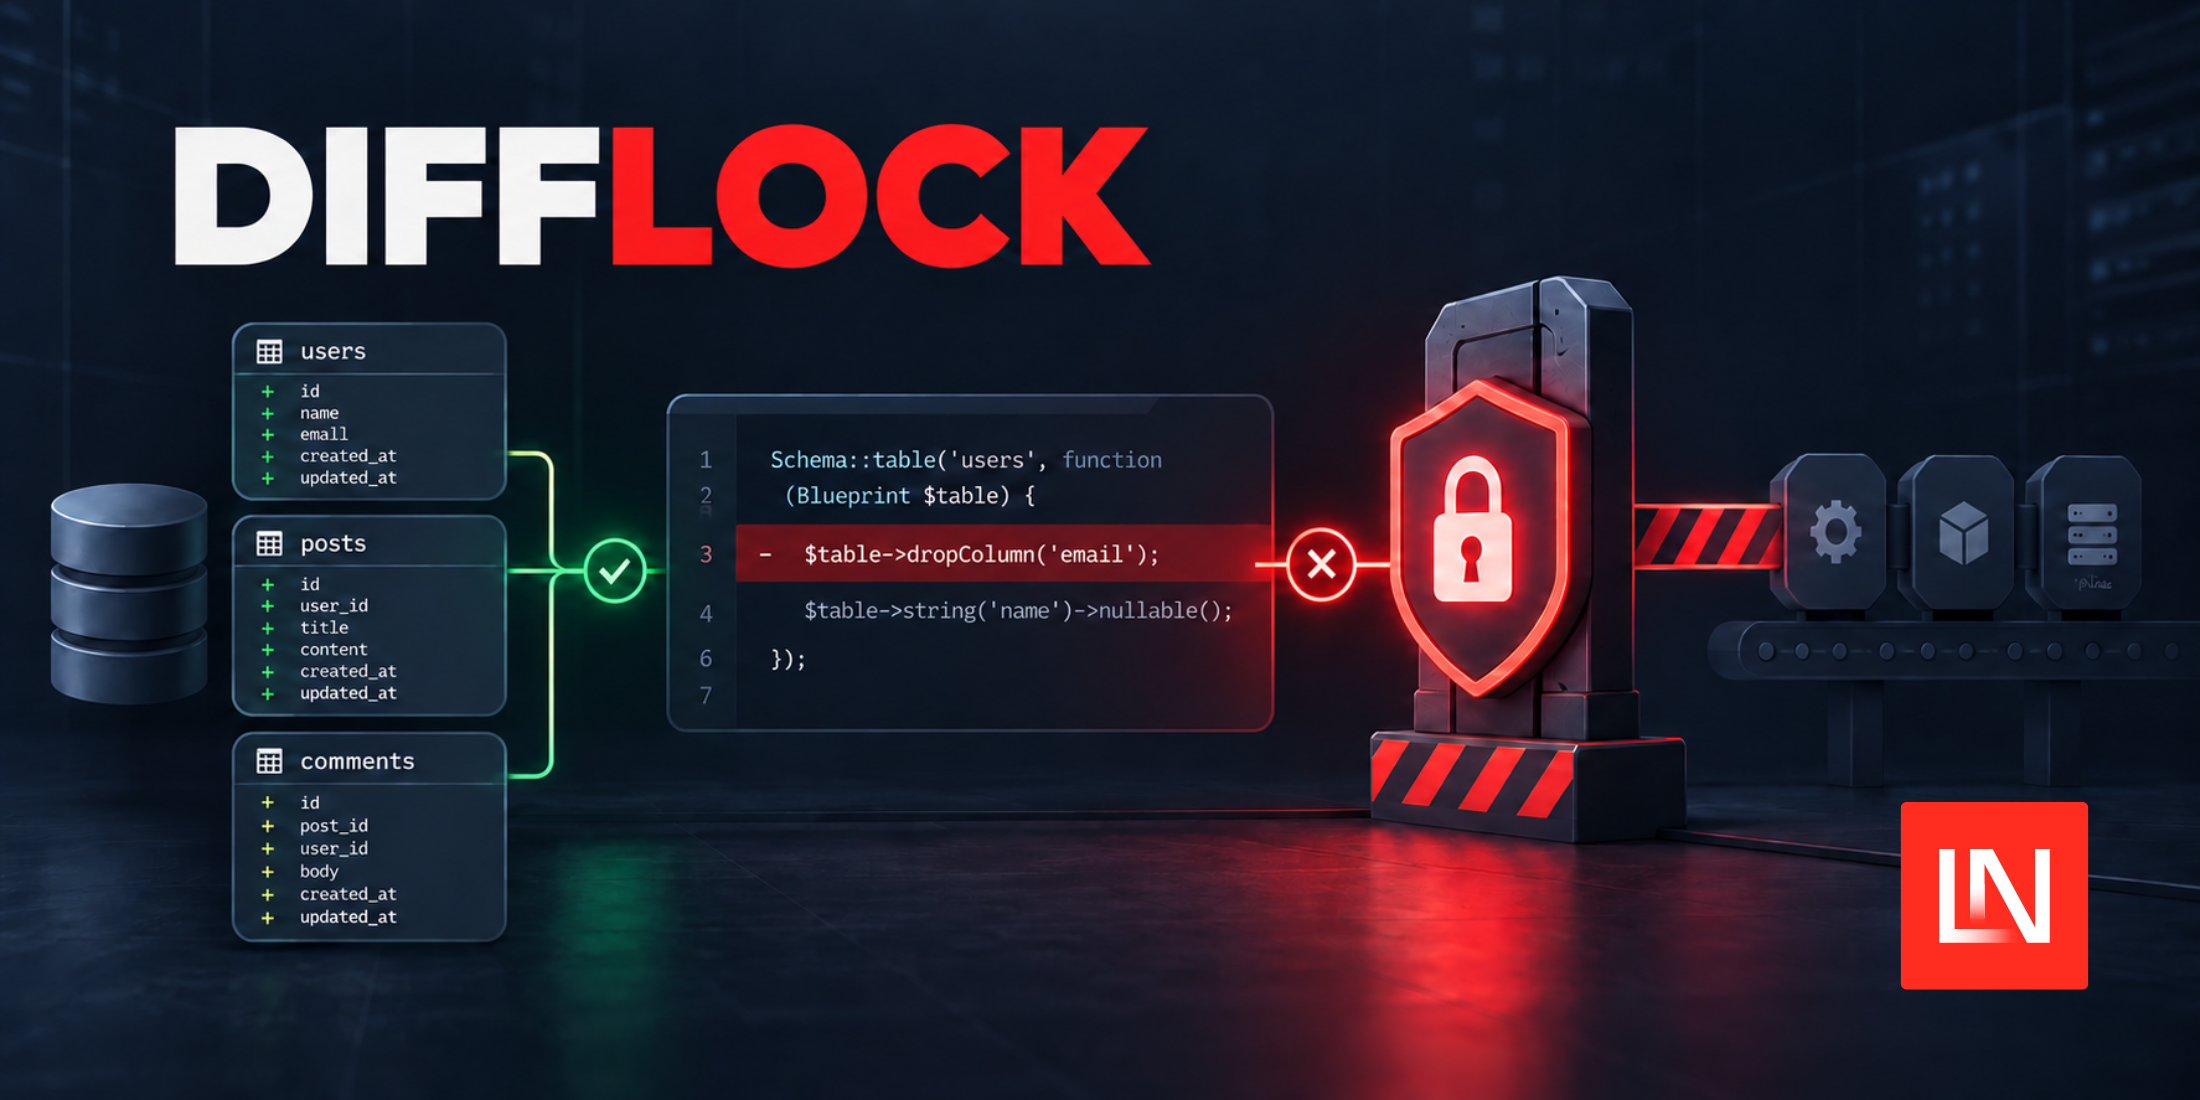
Difflock is a Laravel package that lints pending migrations against the live database schema, records schema baselines as JSON, and provides CI‑compatible guards to prevent risky migrations. It offers commands for linting, diffing, guarded migration execution, and an MCP server for agent‑driven checks, supporting MySQL, PostgreSQL, SQLite, and more.

  • Difflock parses migration files without executing them and compares changes to the actual live schema, flagging destructive ops, column changes, missing indexes, and sensitive columns.
  • It can generate a JSON schema snapshot (`schema.json`) to serve as a baseline for drift detection across environments (e.g., staging vs production).
  • A dedicated `difflock:migrate` command runs the lint checks before invoking Laravel’s native migration, aborting on findings that exceed a configurable block level.
  • CI integration is provided via `difflock:check --ci`, which exits with distinct codes for pass, drift/risky findings, and execution failures.

Database schema changes are a common source of production incidents, especially when migrations are written without full visibility into the current schema. Difflock adds a safety net that catches destructive or unintuitive changes early, integrates with CI pipelines, and provides a reproducible sc…

6/10
Related reading

  1. Laravel Scalpel Scans for Filesystem Intrusion Evidence

    Laravel Scalpel is a Laravel‑native scanner that looks for post‑deployment filesystem tampering – rogue PHP files, obfuscated backdoors, altered .htaccess/.user.ini, missing or mis‑configured .env, and diffs against a signed baseline. It ships with six built‑in scanners, baseline snapshot commands, fast vs strict hashing modes, CI‑friendly output (JSON, SARIF, GitHub annotations) and a ScanFinish…

    Laravellaravel-news.com5 min
  2. App Hardening: One Obfuscation Pipeline Across Every Port

    Codename One adds a cloud‑side hardening step that runs on the merged JAR before it is split into Android, iOS, JavaScript, and desktop binaries. It can rename symbols, encrypt string literals, and insert opaque‑predicate control‑flow guards at configurable levels (off → standard → aggressive → paranoid). The transforms are selective per platform to avoid breaking optimizers, and a mapping is kep…

    CodeName Onecodenameone.com6 min
  3. Laravel Vet: Review Composer Code Before It Installs

    Laravel Vet is a Composer plugin that intercepts installs/updates, shows the diff of each package, and lets you approve changes manually or via an LLM‑based coding agent. Trusted packages are recorded in a `vet.json` with a content hash, so future updates only prompt for new changes. The tool exits with an error on untrusted code, making it CI‑friendly, and works with any PHP project using Compos…

    Laravellaravel-news.com4 min
  4. CloudBees vs Harness: Why Migration Isn't the Fix

    The article argues that Harness’s “free migration” offer hides significant downstream costs (training, pipeline rebuilds, compliance recertification) and that even after migration you still lack unified governance across heterogeneous CI/CD tools. CloudBees positions its Unify control plane as a tool‑agnostic layer that adds visibility, continuous governance, AI‑driven test selection, and hybrid…

    Codeshipcloudbees.com5 min