Related reading
Laravel Scalpel Scans for Filesystem Intrusion Evidence
Laravel Scalpel is a Laravel‑native scanner that looks for post‑deployment filesystem tampering – rogue PHP files, obfuscated backdoors, altered .htaccess/.user.ini, missing or mis‑configured .env, and diffs against a signed baseline. It ships with six built‑in scanners, baseline snapshot commands, fast vs strict hashing modes, CI‑friendly output (JSON, SARIF, GitHub annotations) and a ScanFinish…
Laravellaravel-news.com5 minIntroducing ClickHouse's new TimeSeries Engine: Your drop-In Prometheus replacement
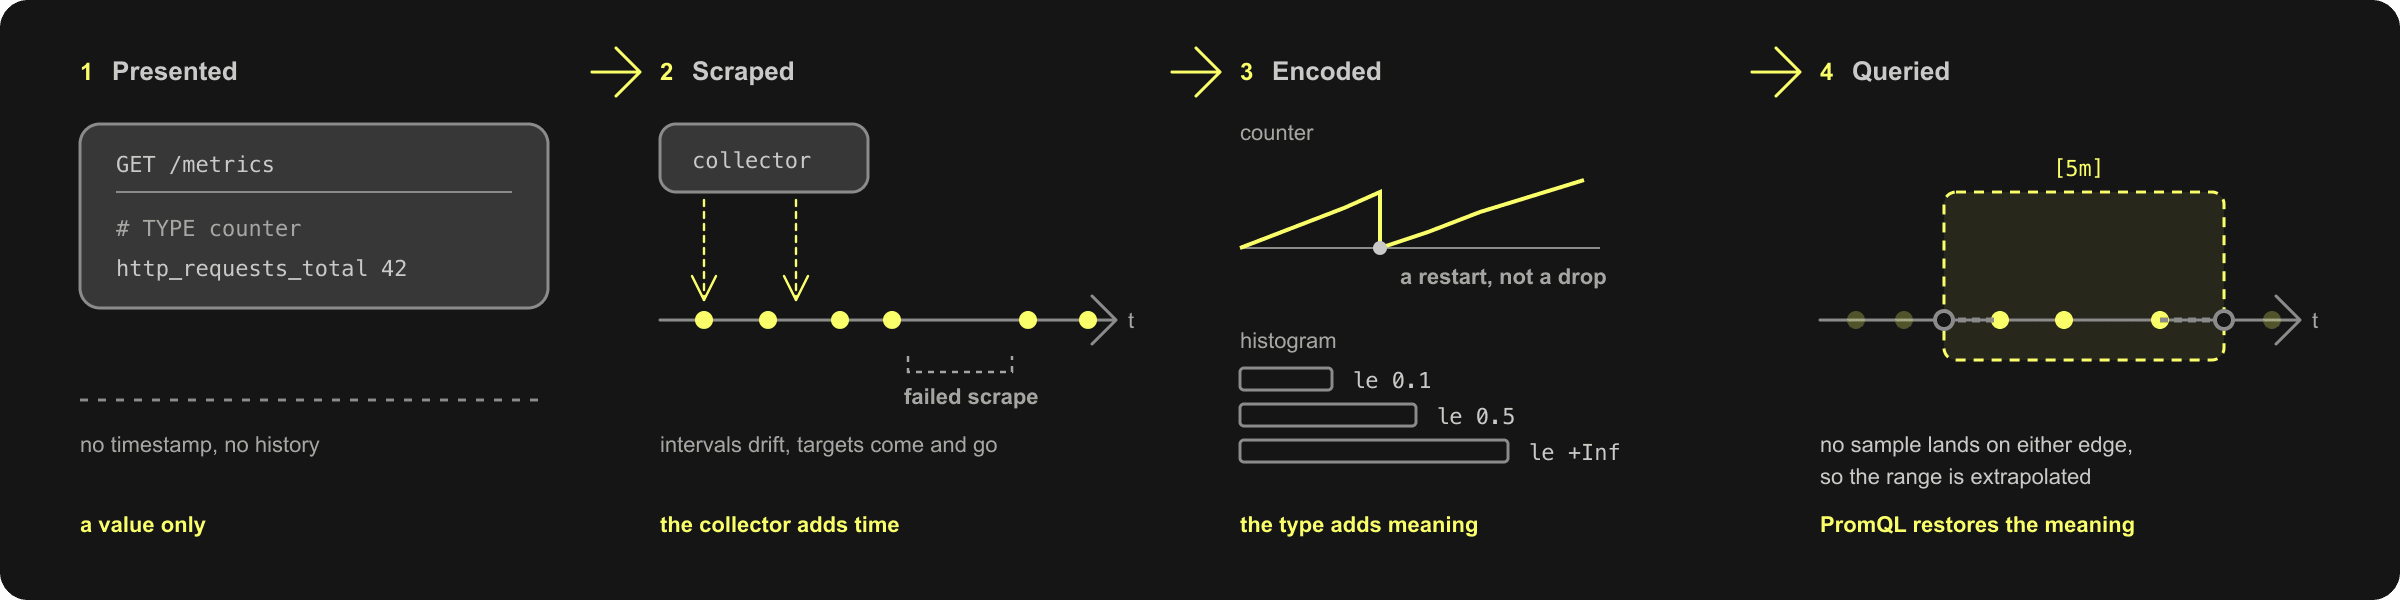
ClickHouse Cloud adds a private‑preview TimeSeries engine that ingests Prometheus remote‑write data and serves it via native PromQL, letting you keep existing PromQL queries while storing metrics in ClickHouse.
ClickHouseclickhouse.com10 minHN2July in Servo: more platforms, faster canvas, web fonts in SVG, and more!
Servo 0.5.0 (July 2026) ships 488 commits, adds Linux aarch64 binaries, a slew of CSS/DOM/WebGPU features, new SubtleCrypto curves, accessibility performance tweaks, security patches for quick‑xml and crossbeam‑epoch, and real‑world fixes for DuckDuckGo and Gumroad.
Mozilla Automation Teamservo.org9 minHN51September 16, 2026 security incident: how we responded to a LiteSpeed zero-day attack
Hostinger detected a zero‑day exploit in LiteSpeed Web Server on a Brazil server on Sep 16 2026, giving the attacker root access and compromising 399 accounts. The team isolated the server, coordinated with LiteSpeed to patch the vulnerability, rolled out the fix fleet‑wide, and restored affected sites from backups within the same day.
Hostingerhostinger.com2 minpostmortem