Related reading
Kubernetes 1.37 Released: Stable Metrics API and Rootless Kubelet in Beta
Kubernetes 1.37 (Garhwal) ships GA Metrics API, beta rootless kubelet, GA resilient watchcache, GA pod certificates, and a suite of alpha/beta features (workload‑aware scheduling, pod checkpoint/restore, StatefulSet Recreate strategy). The release focuses on stability, security, and AI/ML cost‑optimisation.
InfoQinfoq.com2 minreleaseKubernetes v1.37: Pod-Level Resource Managers graduated to Beta
Kubernetes v1.37 adds Pod‑Level Resource Managers to beta (off by default). The feature lets Kubelet’s Topology, CPU, and Memory managers consume pod‑level `.spec.resources` to reserve exclusive NUMA‑aligned CPUs/memory for primary containers while sidecars share a pod‑isolated pool. A new PodResources gRPC API now reports `cpu_ids` and `memory` per pod. Enable via the `PodLevelResourceManagers`…
Kuberneteskubernetes.io2 minKubernetes v1.37: Hardening Container Storage with Bind Mount Options and EmptyDir Permissions
Kubernetes v1.37 adds two alpha‑level storage hardening knobs: per‑volume `bindMountOptions` (e.g. noexec, nosuid, nodev) that affect the bind‑mount the runtime creates, and an `emptyDir` `mode` field to set Unix permission bits (including the sticky bit). Together they let you enforce least‑privilege policies on writable volumes without init‑containers or CSI tricks.
Kuberneteskubernetes.io8 minHN3Monitor TAS and gang scheduling for AI training in Kubernetes
Kubernetes’ default scheduler can’t satisfy AI training’s need for low‑latency GPU interconnects and simultaneous pod start‑up. The blog explains how the open‑source Kueue job queue adds topology‑aware placement (using node labels like `topology.kubernetes.io/rack`) and how the Coscheduling plugin adds a permit phase that only binds a gang of pods when the full set is ready, preventing idle GPU r…
Datadogdatadoghq.com19 minTransform and route security logs to Microsoft Sentinel tables using Observability Pipelines
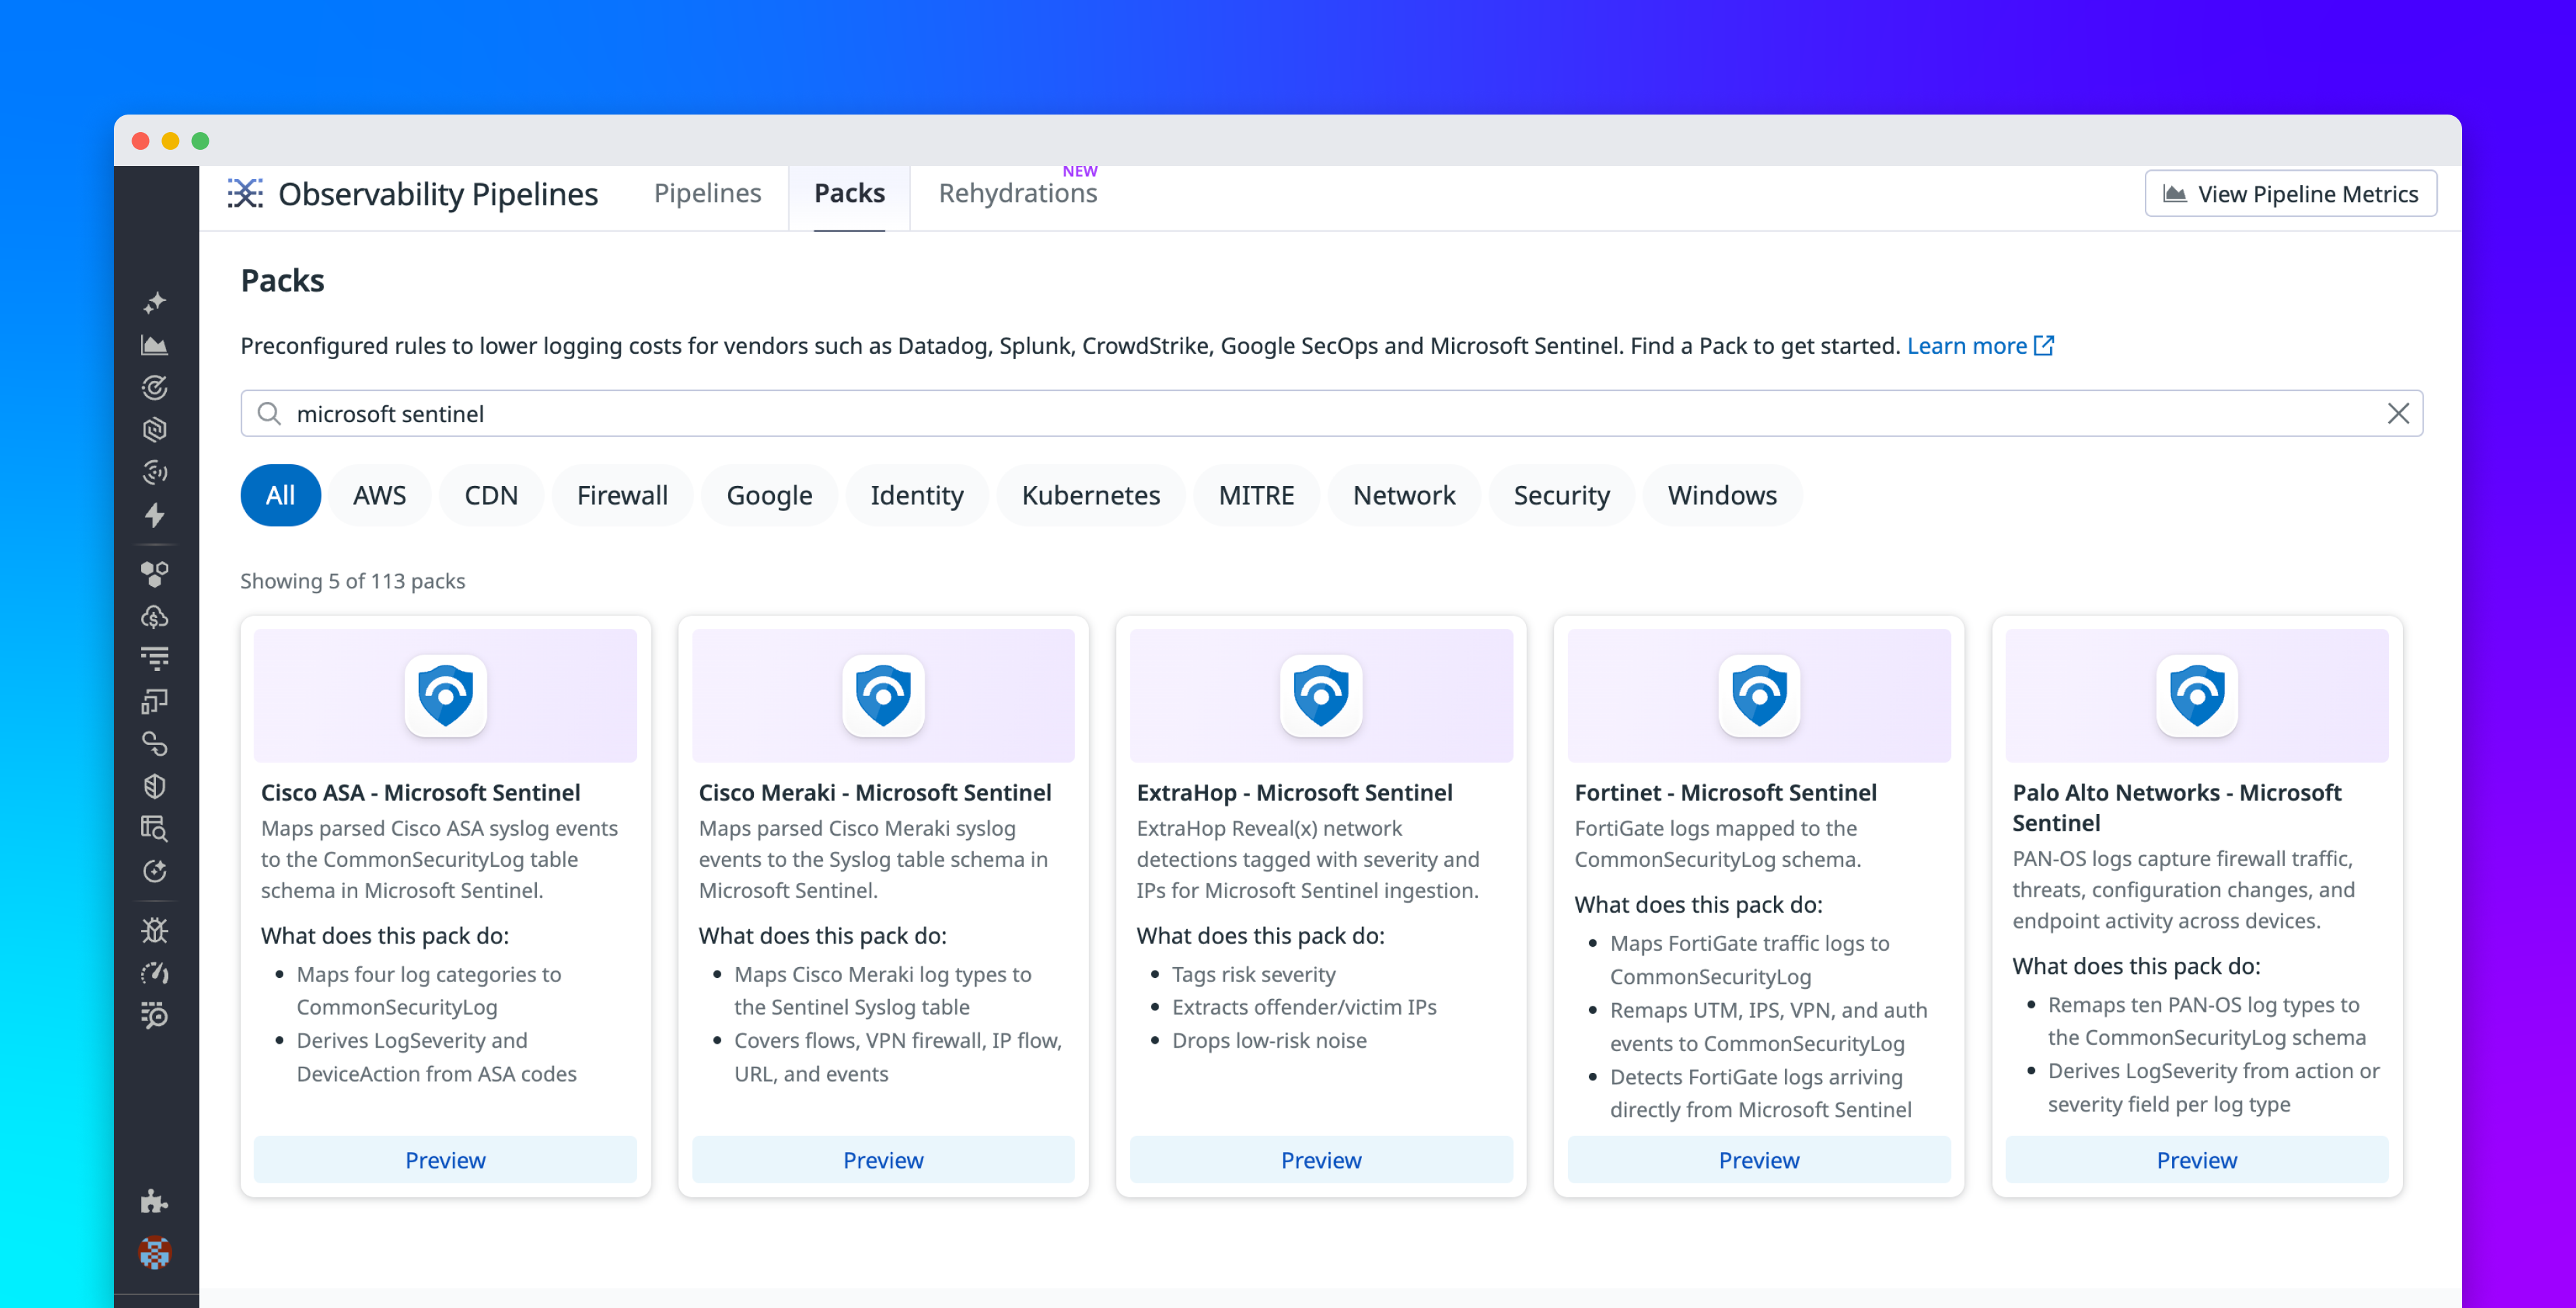
Datadog Observability Pipelines now ships pre‑built Microsoft Sentinel Packs that map logs from Palo Alto, Fortinet, Cisco ASA, Cisco Meraki, and ExtraHop into Sentinel’s CommonSecurityLog or Syslog tables. Packs handle field extraction, severity derivation, and device‑action mapping, letting you filter or drop low‑value events before ingest, validate mappings with Live Capture, and reduce per‑GB…
Datadogdatadoghq.com5 min