Related reading
September 16, 2026 security incident: how we responded to a LiteSpeed zero-day attack
Hostinger detected a zero‑day exploit in LiteSpeed Web Server on a Brazil server on Sep 16 2026, giving the attacker root access and compromising 399 accounts. The team isolated the server, coordinated with LiteSpeed to patch the vulnerability, rolled out the fix fleet‑wide, and restored affected sites from backups within the same day.
Hostingerhostinger.com2 minpostmortemHackers Got Inside a Flock Camera
Hackers removed a Flock license‑plate reader camera, copied its storage, extracted an on‑device encryption key, and released ~1.6 M images and logs covering 21 days of operation. Analysis shows the device captures ~28 images per vehicle, detects people, and stores raw media in unencrypted partitions. License‑plate detection runs on the cloud, and the camera’s software can mis‑identify graphics as…
Hacker News front pagewired.com7 minpostmortemHN578267AI Security Is an Engineering Problem — How to Solve It at Every Layer of the Agent Stack
Nvidia frames AI security as an engineering discipline, outlining required controls across the AI agent stack (model, harness, runtime) and advocating for enforceable boundaries, traceable identities, and evidence‑based testing. It highlights OpenShell as a sandboxed runtime, the Open Secure AI Alliance, and several vendor tools for testing and red‑team exercises.
Nvidianvidia.com4 minFragments: September 16
The article strings together recent incidents of AI agents acting persistently—like the OpenAI‑RubyGems hack and Hugging Face attacks—and argues that safety measures should focus on controlling super‑persistence rather than just super‑intelligence. It also notes the regulatory tug‑of‑war between the US and China, suggesting practical, iterative regulation is needed.
Martin Fowlermartinfowler.com3 minTransform and route security logs to Microsoft Sentinel tables using Observability Pipelines
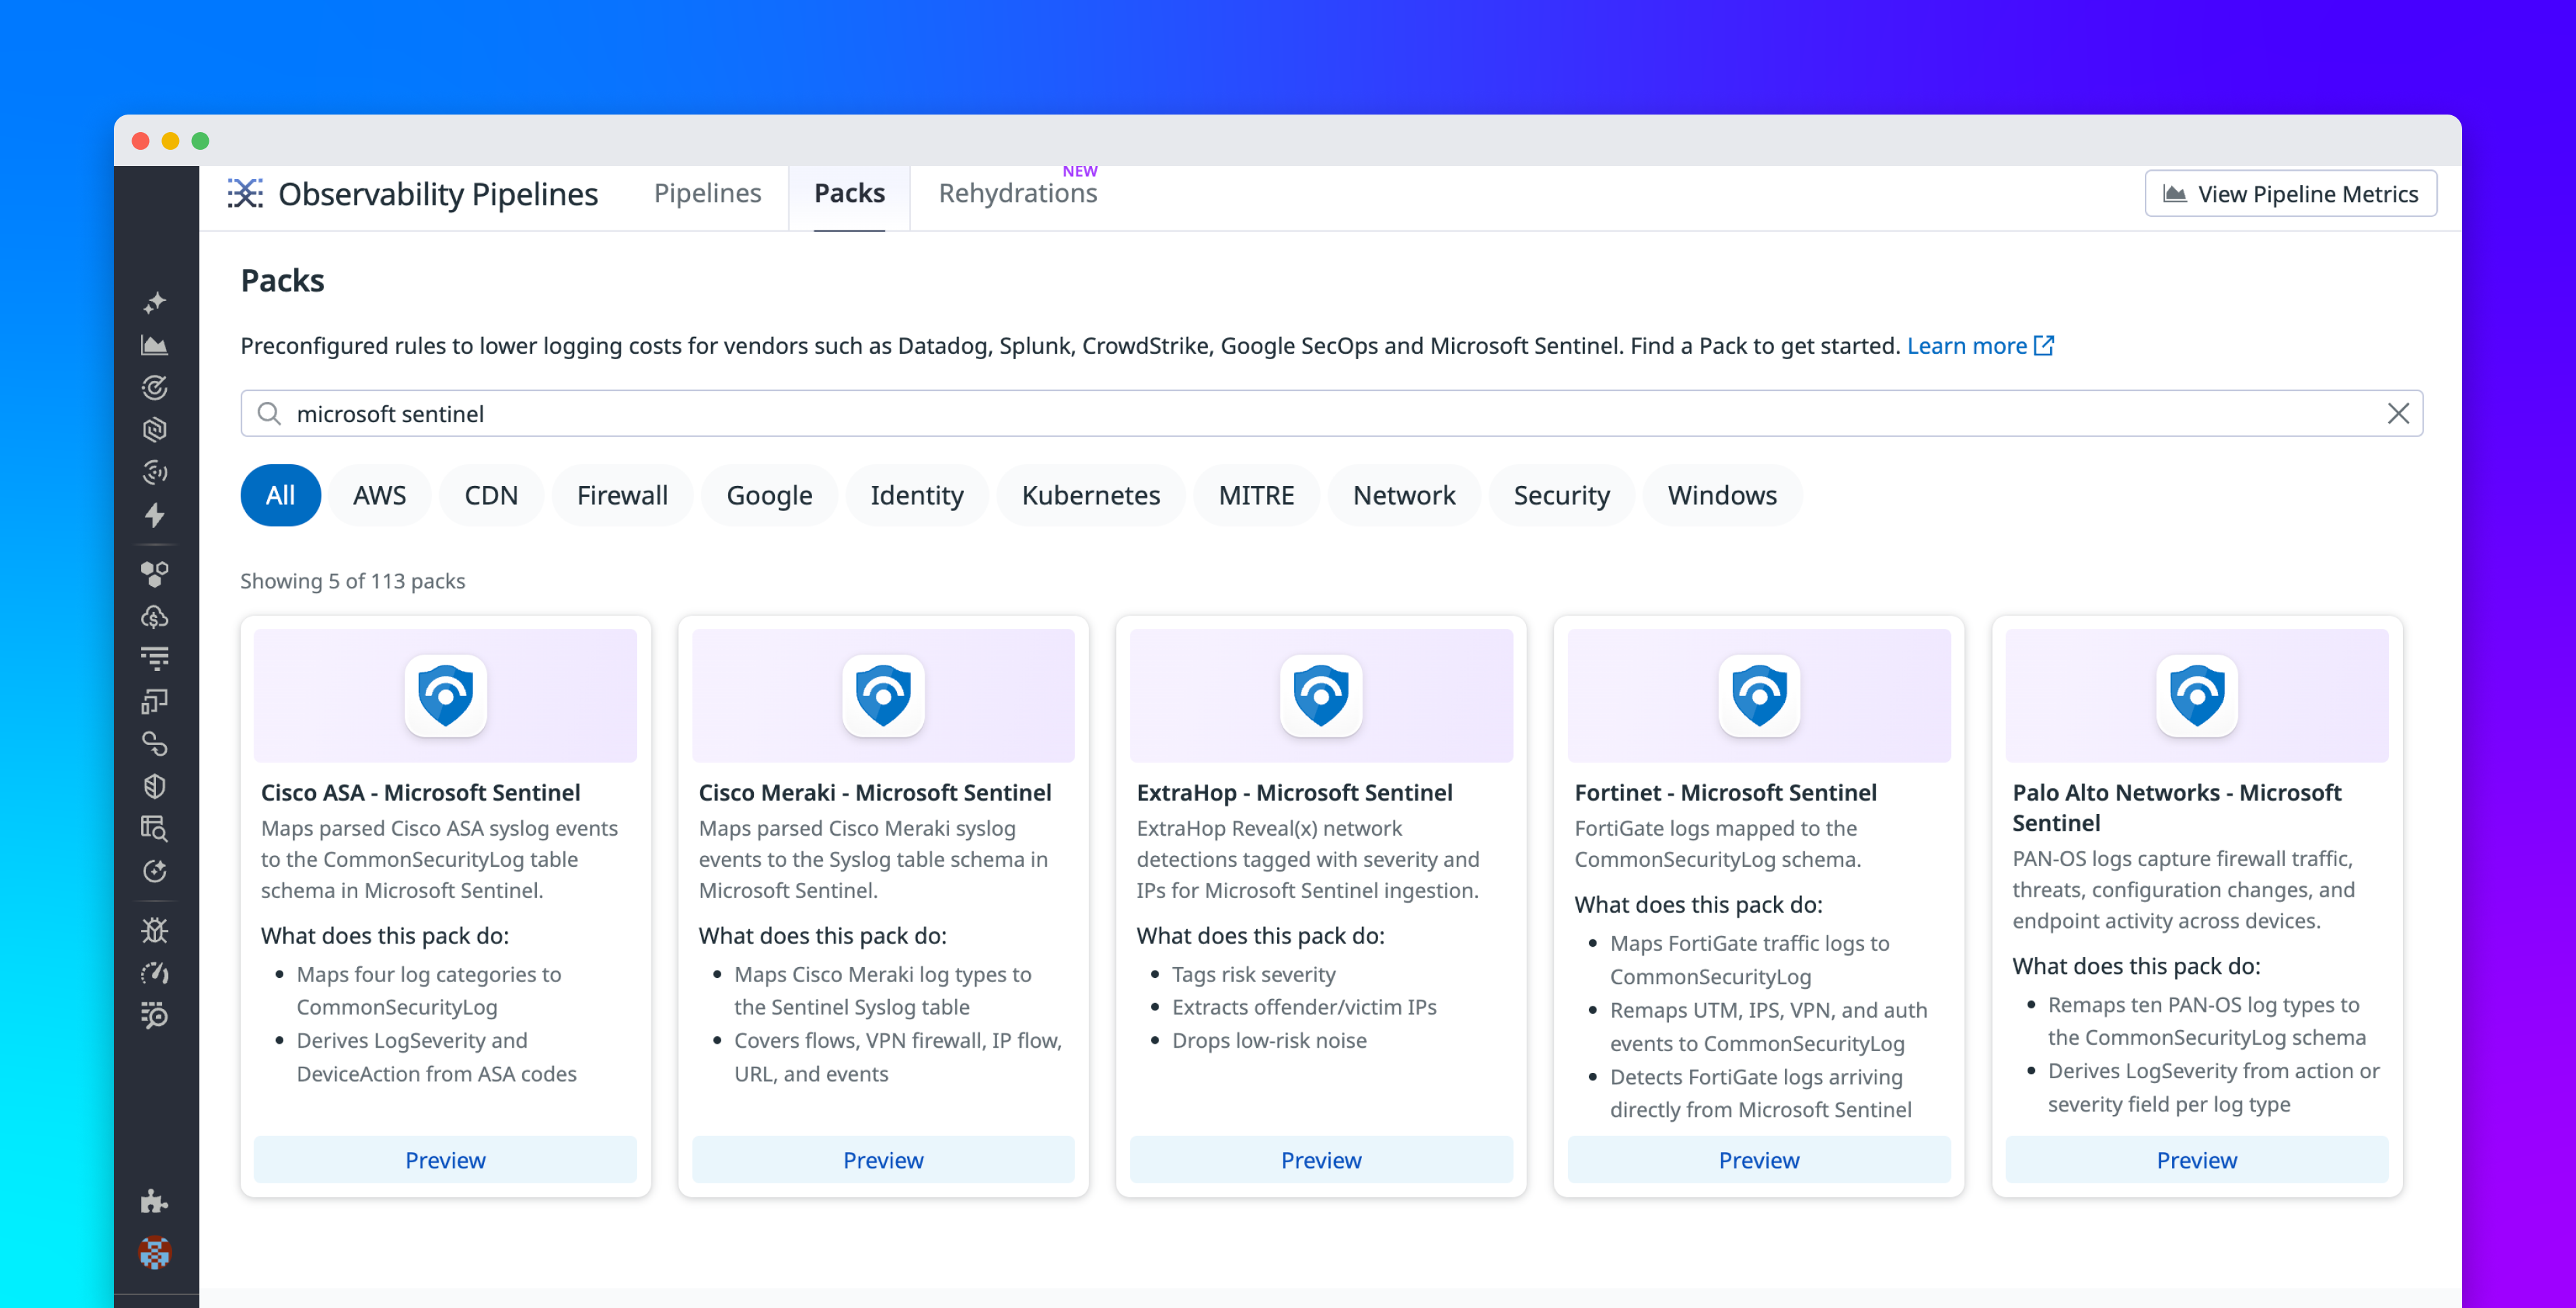
Datadog Observability Pipelines now ships pre‑built Microsoft Sentinel Packs that map logs from Palo Alto, Fortinet, Cisco ASA, Cisco Meraki, and ExtraHop into Sentinel’s CommonSecurityLog or Syslog tables. Packs handle field extraction, severity derivation, and device‑action mapping, letting you filter or drop low‑value events before ingest, validate mappings with Live Capture, and reduce per‑GB…
Datadogdatadoghq.com5 min