Related reading
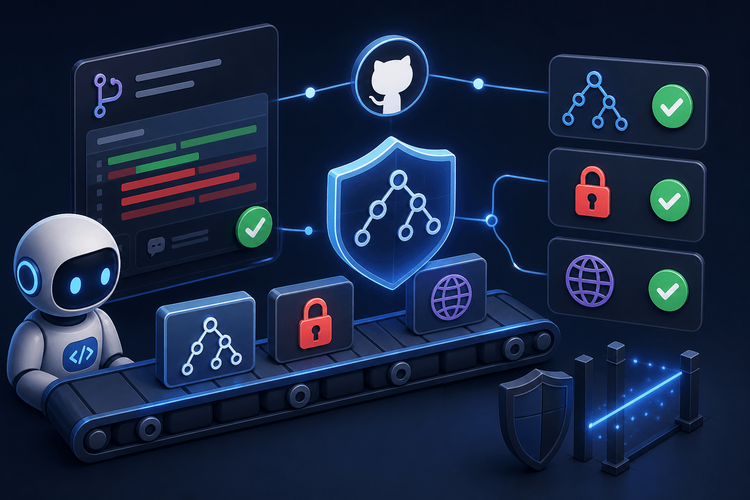
Securing AI Pull Requests: Building a Deterministic AST Audit Harness in GitHub Actions
A step‑by‑step tutorial for building a deterministic AST‑based security scanner that runs in GitHub Actions to catch prototype‑pollution, high‑entropy secrets, and unauthorized network egress in AI‑generated pull requests.
SitePointsitepoint.com19 minArticle: Beyond Relevance: A Governance-First Architecture for Enterprise Personalization
The article proposes a governance‑first architecture for enterprise personalization, where policy‑driven steps (memory, journey graph, AI routing, scoring, trust checks, outcome simulation) shape the recommendation before it is returned. A reference FastAPI implementation demonstrates the pattern with external YAML policies and optional LLM assistance.
InfoQinfoq.com19 minApp Hardening: One Obfuscation Pipeline Across Every Port
Codename One adds a cloud‑side hardening step that runs on the merged JAR before it is split into Android, iOS, JavaScript, and desktop binaries. It can rename symbols, encrypt string literals, and insert opaque‑predicate control‑flow guards at configurable levels (off → standard → aggressive → paranoid). The transforms are selective per platform to avoid breaking optimizers, and a mapping is kep…
CodeName Onecodenameone.com6 minHidden Technical Debt in Machine Learning Systems
This paper introduces the concept of technical debt in machine learning systems, arguing that ML systems accrue unique and significant maintenance costs beyond traditional software engineering. It identifies several ML-specific risk factors like entanglement, hidden feedback loops, and data dependencies that erode system boundaries and increase long-term operational expenses.
Hall of Famenips.cc25 minpaper