proomt

Search

Search posts, papers, and topics

All posts

SitePoint19 min readtutorialintermediate

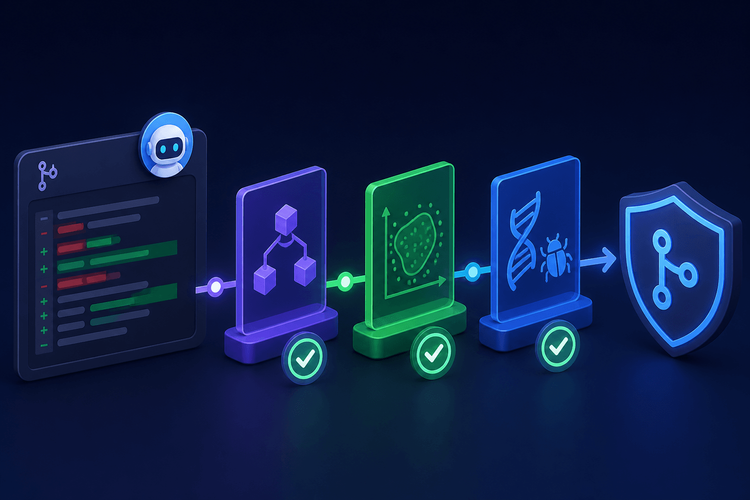
Securing AI Pull Requests: Building a Deterministic AST Audit Harness in GitHub Actions

Summary

A step‑by‑step tutorial for building a deterministic AST‑based security scanner that runs in GitHub Actions to catch prototype‑pollution, high‑entropy secrets, and unauthorized network egress in AI‑generated pull requests.

  • Use @babel/parser + @babel/traverse to get a full‑fidelity TypeScript AST and run independent visitors for each threat class.
  • Prototype‑pollution detection relies on scope‑aware analysis of computed property assignments (e.g., obj[key] = … where key may be "__proto__").
  • Secret detection computes Shannon entropy on every StringLiteral/TemplateLiteral node to flag high‑entropy values, catching base64 or atob‑encoded tokens.
  • Egress detection tracks fetch/axios/http calls and dynamic import() arguments against a configurable allow‑list, rejecting any outbound URL.

AI code generators can inject subtle, runtime‑only vulnerabilities that static linters miss. A deterministic, AST‑driven audit gives reproducible, language‑aware security checks that can be enforced automatically at merge time.

6/10
Related reading

  1. GPT-6 Astra Is the First Model OpenAI Classifies as Critical for Cybersecurity

    OpenAI labeled GPT‑6 Astra as “Critical” for cybersecurity under its Preparedness Framework – the first model to meet that bar. In controlled tests the model autonomously discovered zero‑day bugs in a browser and an OS kernel, building working exploit chains in 29 h (browser) and 12 h (kernel). A benchmark of post‑cutoff vulnerabilities confirmed its ability to find unknown flaws. OpenAI reports…

    InfoQinfoq.com3 min
  2. Changing the game: How Google uses agentic AI to secure hundreds of millions of lines of code

    Google’s AI & Infrastructure team built an agentic pipeline (Mantis) that runs pre‑submit AI‑driven scans on every code check‑in, validates findings with a fast triage agent (AST + call‑graph analysis) achieving >92% precision in <1 min, then auto‑generates fixes via a bug‑fix agent. Localized threat models and a two‑step scan cut false‑positives to ~3% and prevent hundreds of vulnerabilities eac…

    Google Cloud Bloggoogle.com4 min
  3. We now auto-approve and merge 15% of PRs

    This article describes how a team implemented a bot to auto-approve and merge 15% of low-risk pull requests, aiming to reduce code review bottlenecks and improve development velocity. The system relies on custom deterministic linters, basic end-to-end tests, and a risk scoring mechanism to identify safe changes.

    Swizec Tellerswizec.com3 min