proomt

Search

Search posts, papers, and topics

All posts

InfoQRenato Losio2 min readintermediate
AI Agents Are Disrupting Open Source Security Disclosure

Summary

AI agents can turn minimal public hints about software bugs into working exploits, rendering traditional embargoes ineffective. The article cites a study where a GPT‑4 agent exploited 87% of a 15‑vulnerability benchmark from CVE descriptions and discusses faster releases and revocable capabilities as mitigations.

  • AI agents can generate exploits from limited public clues, making embargo periods almost irrelevant.
  • A GPT‑4‑based study showed 87% success exploiting 15 CVE‑described bugs versus 7% without descriptions.
  • Opening a PR can trigger exploit attempts within minutes, pressuring maintainers to release patches faster.
  • Proposed mitigations include private vulnerability coordination, continuous rapid releases, and revocable capability protocols.

Open‑source maintainers and security teams must adapt disclosure and release practices because AI can rapidly turn hints into exploits.

6/10
Related reading

  1. Confused Deputy: The Old Bug That AI Agents Keep Reintroducing

    The Confused Deputy problem—where a privileged component is tricked into misusing its authority—has resurfaced in AI agents that process natural‑language prompts. The article shows real 2026 attacks, explains why agents are especially vulnerable, and outlines mitigations like least‑privilege scopes, capability‑based tokens, and human‑in‑the‑loop approvals.

    Auth0auth0.com9 min
  2. Changing the game: How Google uses agentic AI to secure hundreds of millions of lines of code

    Google’s AI & Infrastructure team built an agentic pipeline (Mantis) that runs pre‑submit AI‑driven scans on every code check‑in, validates findings with a fast triage agent (AST + call‑graph analysis) achieving >92% precision in <1 min, then auto‑generates fixes via a bug‑fix agent. Localized threat models and a two‑step scan cut false‑positives to ~3% and prevent hundreds of vulnerabilities eac…

    Google Cloud Bloggoogle.com4 min
  3. AI Security Is an Engineering Problem — How to Solve It at Every Layer of the Agent Stack

    Nvidia frames AI security as an engineering discipline, outlining required controls across the AI agent stack (model, harness, runtime) and advocating for enforceable boundaries, traceable identities, and evidence‑based testing. It highlights OpenShell as a sandboxed runtime, the Open Secure AI Alliance, and several vendor tools for testing and red‑team exercises.

    Nvidianvidia.com4 min
  4. OpenClaw Is a Preview of Why Governance Matters More Than Ever

    Autonomous AI agents like OpenClaw are shifting software development from AI-assisted to AI-executed, capable of committing code and orchestrating deployments without human approval. This necessitates robust governance to manage increased risks in security, compliance, and accountability, as traditional DevOps assumptions no longer hold.

    Codeshipcloudbees.com6 min
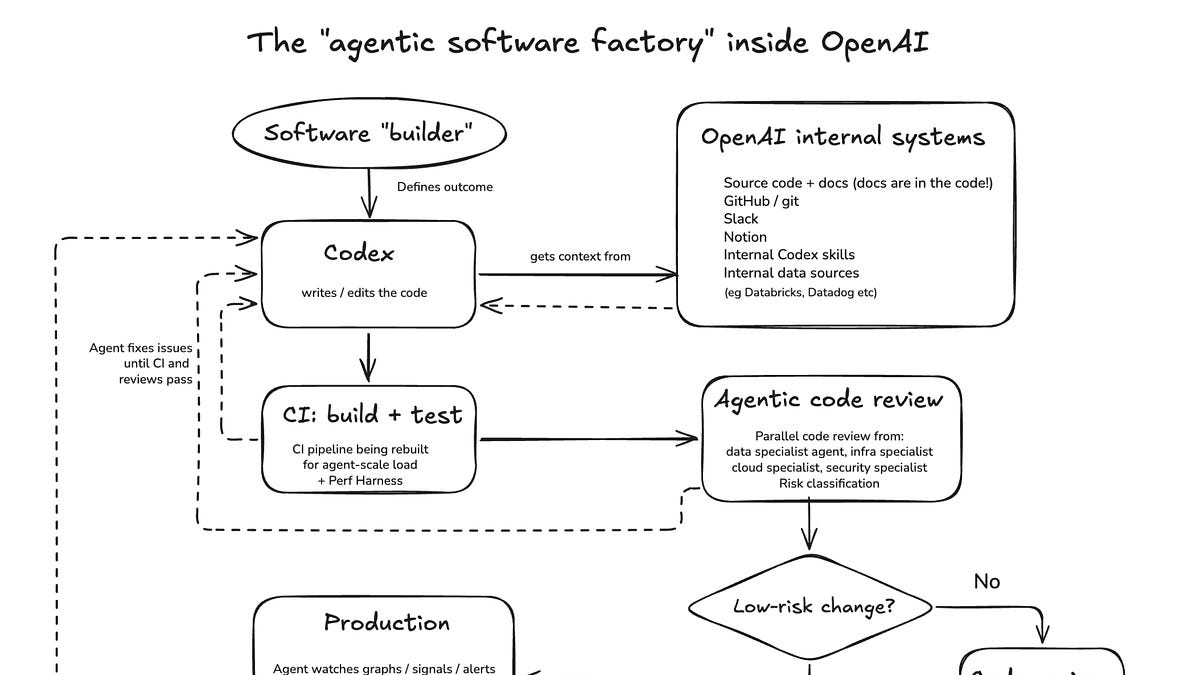
  5. Inside OpenAI’s agentic software factory

    OpenAI has internalized Codex and ChatGPT Work as a universal coding agent, achieving >90% adoption across the company and reshaping tooling, CI/CD load, and engineering roles. The shift has forced a new agentic software factory, massive infra scaling, and a rethink of IDEs, PRs, and code reviews.

    The Pragmatic Engineerpragmaticengineer.com15 minHN1