SitePoint16 min readtutorialintermediate
Automating DevSecOps Static Analysis with GitHub Actions and Agent Skills
Summary
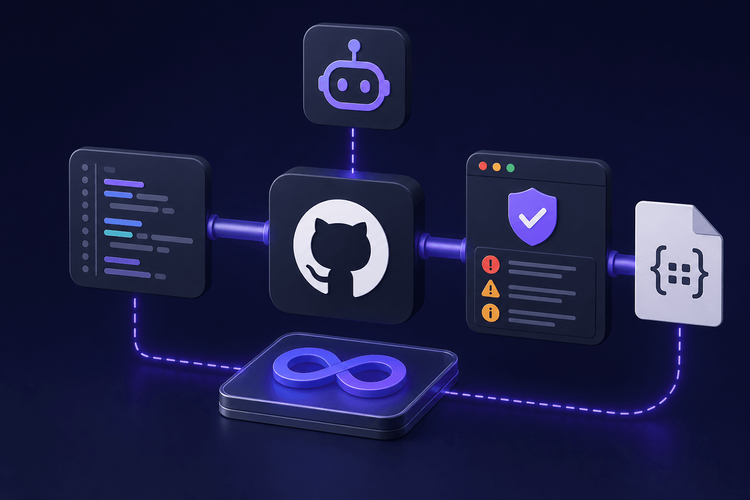
The article shows how to package an AST‑based TypeScript security scanner as an Agent Skill, run it in a GitHub Actions workflow on every PR, and upload SARIF v2.1.0 results to get native inline annotations. It also covers enforcing the scan as a required status check in branch protection.
- Define a SKILL.md manifest to declare inputs, outputs, and sandbox constraints for a reusable static scanner.
- Implement an AST‑based TypeScript scanner using the TypeScript Compiler API to detect secrets, eval, innerHTML, and prototype‑pollution patterns.
- Configure a GitHub Actions workflow that runs the scanner via tsx, outputs SARIF, and uploads it with codeql-action/upload-sarif for inline PR annotations.
- Add the workflow as a required status check in branch protection to make security feedback mandatory.
TypeScript developers and DevSecOps teams who want automated, shift‑left security checks integrated directly into GitHub pull‑request workflows.
6/10