DatadogChakib Hamie5 min readintermediate
Enforce custom rules in Datadog IaC Security scanning
Summary
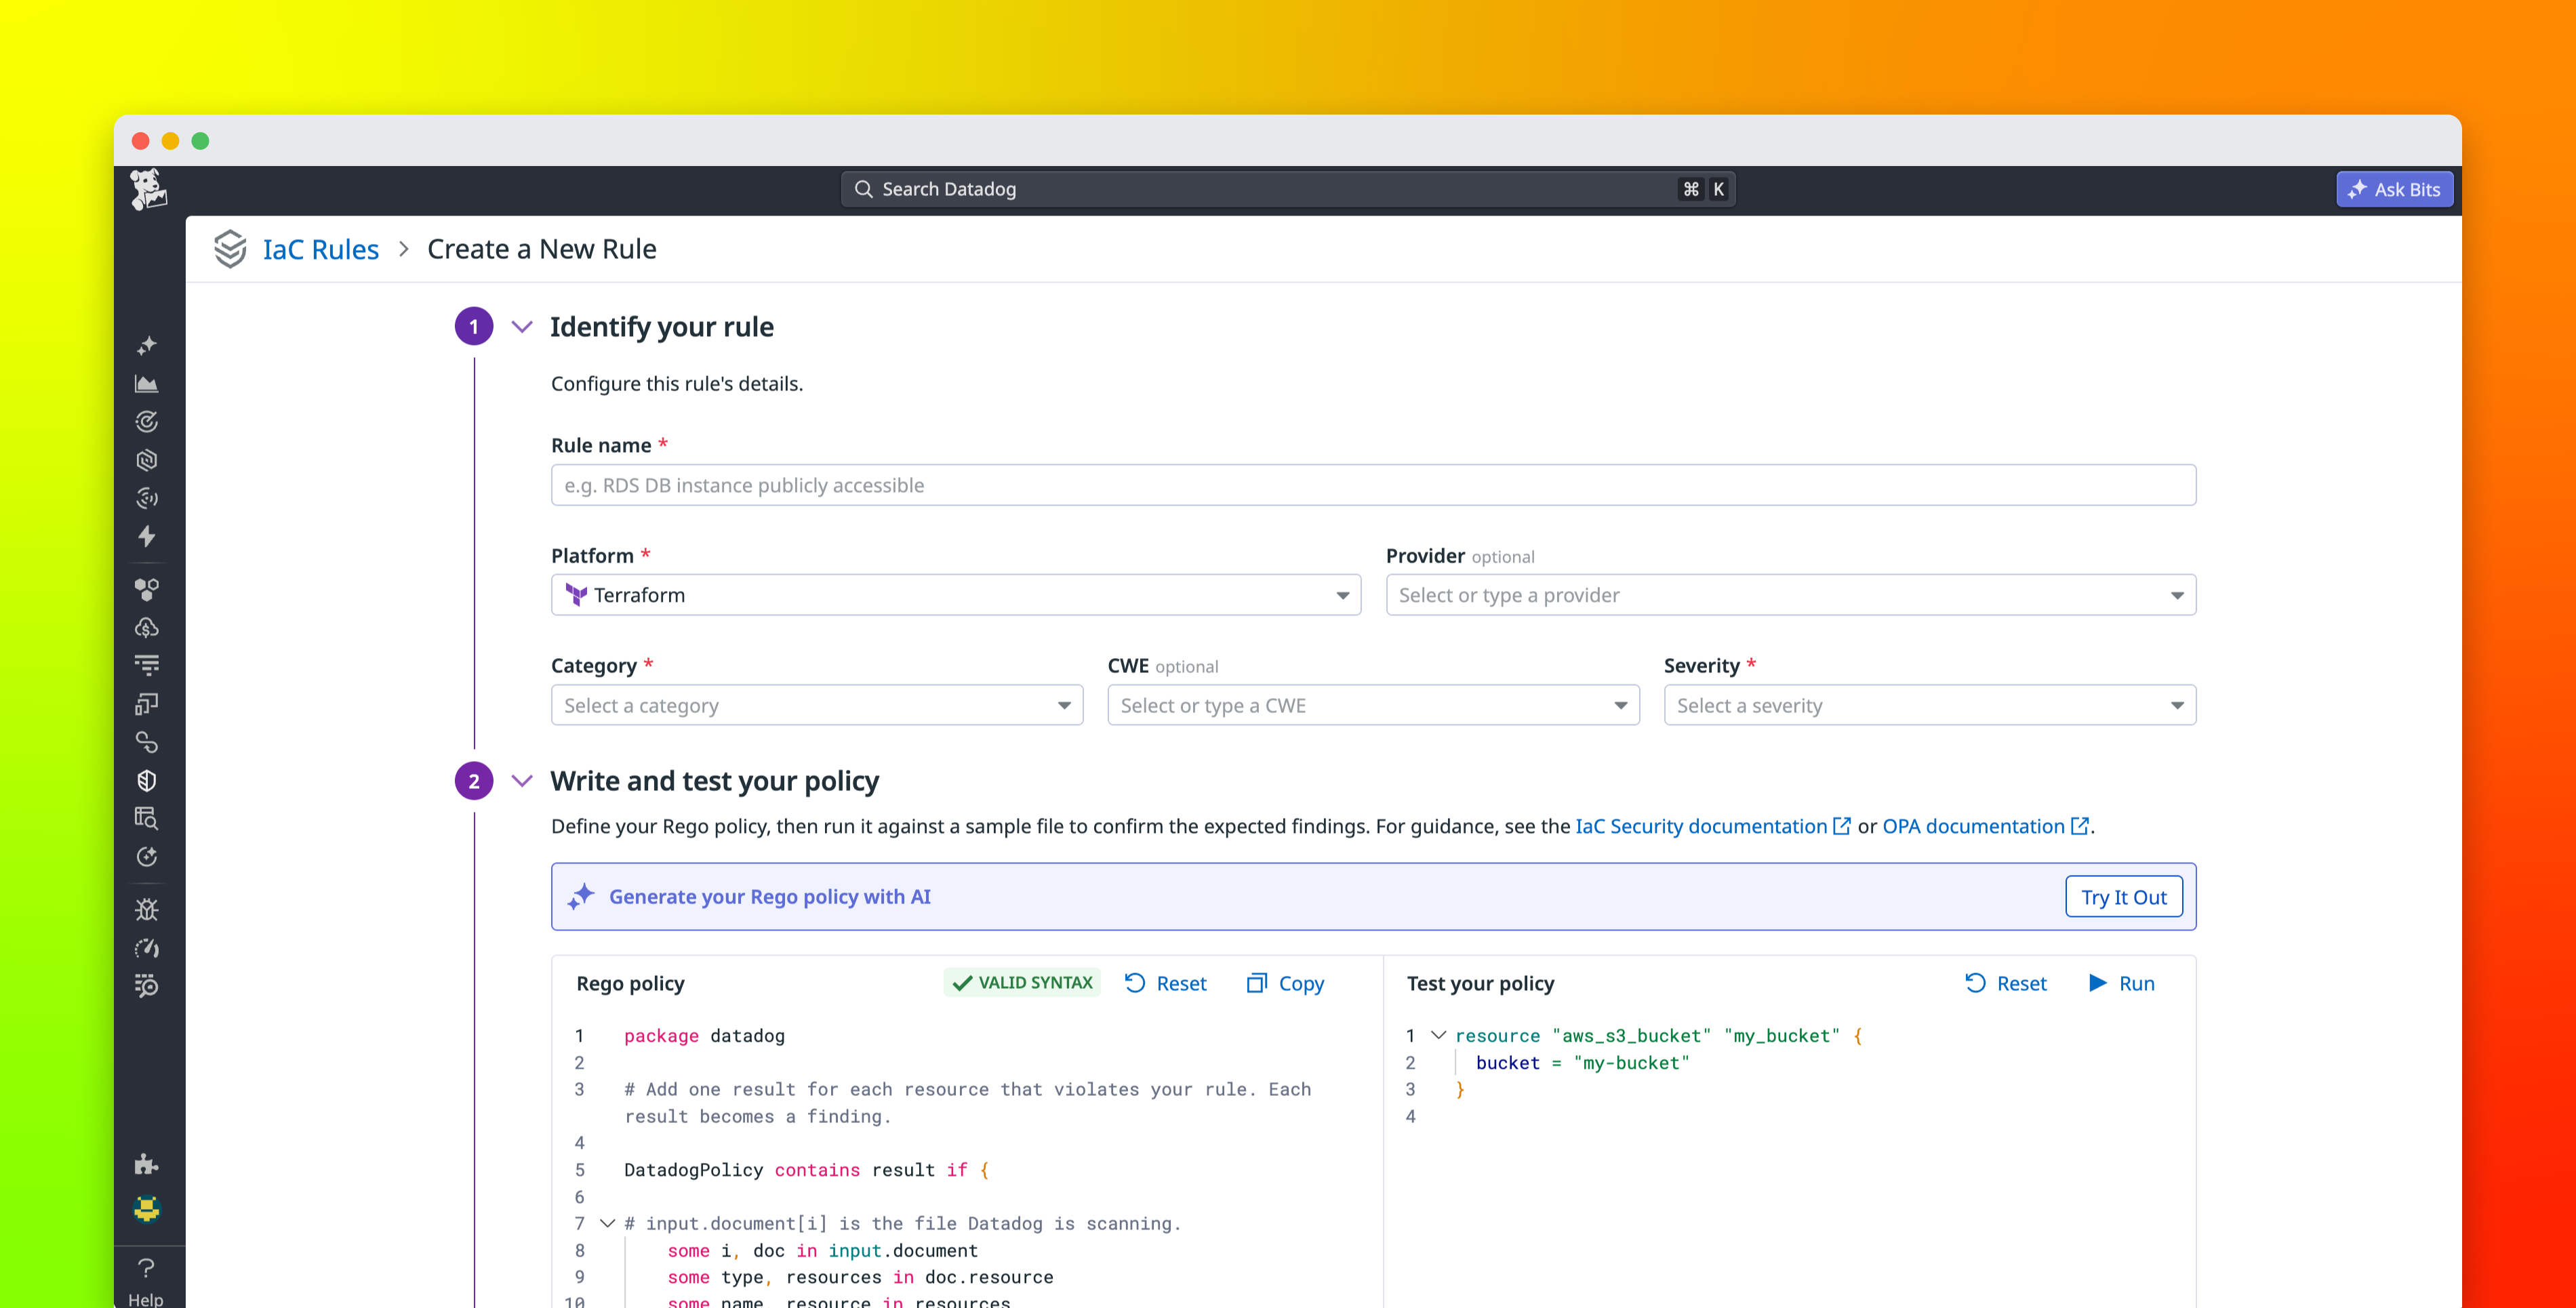
Datadog now lets you write organization‑specific IaC security checks as Rego policies that run alongside its built‑in rule set. You can author, test, version, and publish custom rules via the UI (or AI‑assisted generation), then see violations in PR comments, IDE extensions, or automation pipelines.
- Custom rules are written in OPA’s Rego language and support Terraform, CloudFormation, Ansible, Dockerfile, Kubernetes, and GitHub Actions.
- The UI provides a starter policy, sample IaC file, and an AI‑driven “natural language → Rego” helper; you can also clone existing rules.
- Policies can be evaluated against sample files before publishing, and each edit creates a version with diff/restore capabilities.
- Findings appear in the same workflows as default IaC checks – PR comments, VS Code extension, PR Gates, and Security Automation Pipelines.
Large orgs often have internal IaC standards (tags, approved instance types, naming) that generic scanners don’t cover. Embedding those checks as Rego policies lets security teams enforce compliance early, reduces manual review, and keeps policy changes auditable.
5/10