proomt

Search

Search posts, papers, and topics

devops

RSS
  1. 121

    Setting Up Jenkins EC2 Agents

    The article walks through configuring Jenkins to launch EC2 instances as build agents on demand, covering AWS IAM setup, security groups, key pairs, AMI selection, and the Jenkins EC2 plugin configuration. It shows how idle termination can keep costs low while providing elastic build capacity.

    Codeshipcloudbees.com6 min
  2. 123

    Fine-Grained Access Control Now Available for All Heroku Customers

    Heroku replaces its static role model with per‑app fine‑grained permissions (view, deploy, operate, manage). The new model is exposed via the Dashboard, Heroku CLI (v11.10+), and Platform API, enabling teams to enforce least‑privilege, improve compliance, and automate access provisioning.

    Herokuheroku.com3 minrelease
  3. 124

    Agentic DevOps World 2026: Key Takeaways

    Enterprise AI code generation is outpacing governance: 92% of leaders feel confident but 81% see more production issues; post‑generation stages (review, testing, deployment) are now the bottleneck. Successful adoption requires up‑skilling, end‑to‑end metrics, and tooling (e.g., CloudBees DevOps Agent Kit, PR‑auto‑approval agents).

    Codeshipcloudbees.com8 min
  4. 128

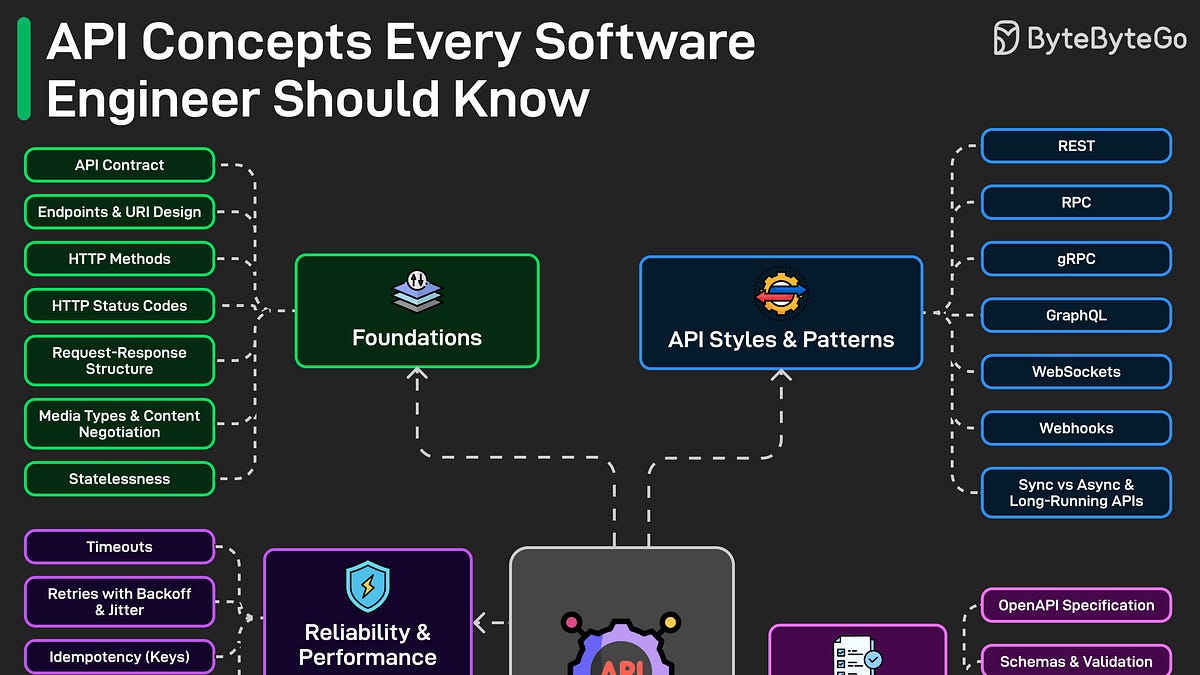
    EP226: API Concepts Every Software Engineer Should Know

    This article outlines essential API design considerations, covering HTTP fundamentals, architectural styles like REST and GraphQL, and critical aspects such as naming, versioning, security, and reliability. It serves as a high-level checklist for engineers designing or consuming APIs.

    ByteByteGobytebytego.com5 min
  5. 130

    AWS Weekly Roundup: AWS Builder Center mobile apps, Amazon Connect Talent GA, Amazon Corretto 27, and more (September 21, 2026)

    AWS’s weekly roundup (Sept 21 2026) bundles a set of product announcements: the Builder Center mobile app (iOS/Android) for browsing courses and workshops; Amazon Connect Talent GA (AI‑driven hiring); Corretto 27 GA (OpenJDK 27 with G1 GC, post‑quantum TLS, compact headers, JFR redaction); Kimi K3 on Bedrock (2.8 T‑param open LLM with vision and 1M‑token context); new T8i burstable EC2 instances…

    AWSamazon.com7 min
  6. 131

    The skills CLI now supports Notion hosted skills

    Vercel’s `skills` CLI (v1.7.0) now lets you install agent skills directly from Notion pages or shared Notion skill packs. Use `npx skills add notion` to browse packs, or `npx skills add <PAGE_URL>` for a single skill. Authentication is handled via the `ntn` CLI, which requires a Notion personal access token. Permissions follow Notion’s page sharing model, so only users with view access can instal…

    Vercelvercel.com1 minrelease
  7. 132

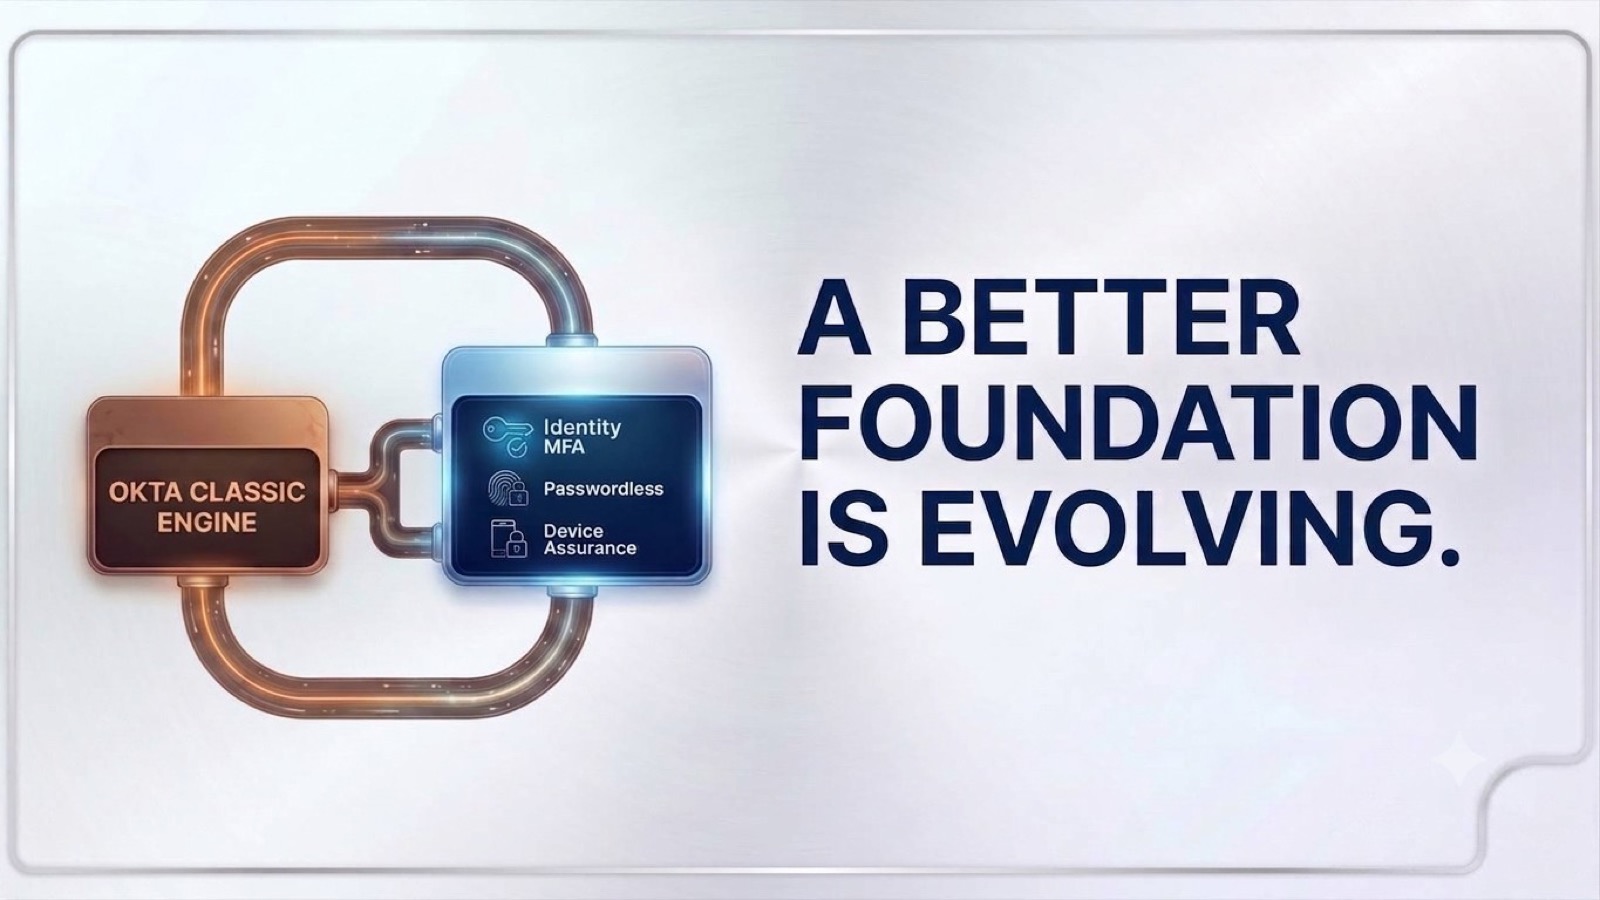
    Classic Engine Feature EOL: SSR, Desktop SSO, Device Trust

    Okta is ending support for Self-Service Registration, Desktop SSO (IWA), and Device Trust on its Classic Engine by March 5, 2027. Users must migrate to Okta Identity Engine to retain these capabilities and gain access to modern security features like passwordless authentication and device assurance.

    Oktaokta.com4 minrelease
  8. 133

    Build Trust on a Short Software Project

    Practical, low‑level habits for earning client trust on short‑duration consulting gigs – rapid feedback loops, visible work, frequent priority checks, early risk surfacing, and leaving the client self‑sufficient.

    Atomic Objectatomicobject.com5 min
  9. 134

    Migrating to Java 17: The Hows, Whys, and Whens

    A product‑focused overview of CloudBees CD/RO’s new integration with Argo Rollouts, describing the supported blue‑green and canary strategies, service‑mesh compatibility, and UI/analytics features. No deep technical walkthrough or performance data.

    Codeshipcloudbees.com6 min
  10. 136

    Every tool is green. Can you ship?

    A CloudBees blog post argues that existing CI, security, and QA tools don’t give release managers a complete view of AI‑generated code risk. It claims tool consolidation rarely helps and proposes a “control plane” (CloudBees Unify) that aggregates signals from multiple tools and adds AI‑driven test prioritization. The piece is largely promotional, with no concrete implementation details, metrics,…

    Codeshipcloudbees.com4 min
  11. 137

    Who Owns AI-Generated Code Failures?

    AI‑generated code breaks the traditional chain of ownership: developers merge PRs they didn’t write, reviewers approve logic they didn’t originate, and QA validates tests chosen by a model. A CloudBees survey shows 81% of firms see more production failures from AI code, and accountability often drifts upward to CTO/VP. The post argues role‑based accountability isn’t enough; you need end‑to‑end tr…

    Codeshipcloudbees.com4 min
  12. 139

    Why engineers should come to the SF Ruby Conference in 2026

    The SF Ruby Conference 2026 is a three‑day event for Ruby engineers, offering AI‑heavy and AI‑light tracks, talks from prominent contributors, and a networking format where every attendee gets a 60‑second mic slot. It provides direct access to experts, hiring opportunities, and community activities for anyone building or scaling Rails applications.

    Evil Martiansevilmartians.com6 min
  13. 141

    Jenkins Configuration as Code: Documentation

    Jenkins Configuration as Code (JCasC) lets you define the Jenkins controller via declarative YAML that mirrors the UI model. The plugin can generate exhaustive documentation and a JSON schema for the YAML, enabling IDE assistance. It also offers a REST API to dry‑run configs before applying them. The post links to related series entries and community resources.

    Codeshipcloudbees.com2 min
  14. 143

    Health Check-up for Your Jenkins

    Kohsuke Kawaguchi outlines a few low‑effort ways to keep a Jenkins instance healthy: use jconsole to watch old‑gen heap usage, the Monitoring plugin (or Nagios) to record HTTP latency and queue length, inspect thread dumps for slow pages, and review the built‑in load chart to spot agent under‑/over‑utilisation.

    Codeshipcloudbees.com3 min
  15. 144

    Introducing ElectricCommander 4.2

    ElectricCommander 4.2 adds a redesigned Resources UI, bulk agent install/upgrade, optional trusted SSL connections, zone‑based segmentation with gateways, new API commands, JSON transport, and a bundled standard license. The release is a typical product update with no deep technical analysis.

    Codeshipcloudbees.com3 minrelease
  16. 145

    Everything is green. Nothing is ready.

    CloudBees Unify is a control‑plane layer that aggregates data from existing CI/CD, security, and release tools to give a single delivery record. It claims to improve test efficiency (98 → 30 min) and enforce governance policies across pipelines, with an AI assistant for incident triage. The post is a product‑focused webinar recap with limited technical depth.

    Codeshipcloudbees.com5 min
  17. 146

    Copying Artifacts Between Builds in a Jenkins Workflow

    The copyartifact plugin now supports Jenkins Pipeline via a core step (v1.34). Use the generic `step([$class: 'CopyArtifact', …])` syntax to pull artifacts from another job, with all existing options available through the Snippet Generator. A native pipeline step is planned.

    Codeshipcloudbees.com1 min
  18. 147

    Best GitLab Alternatives for Enterprise Teams (2026)

    The article is a vendor‑authored marketing piece that lists criteria for picking a GitLab alternative and then promotes CloudBees Unify as a cross‑tool governance layer, with brief mentions of other tools (GitHub, Jenkins, Azure DevOps, Harness, CircleCI). It contains a few quoted survey percentages but no technical deep‑dive, code, architecture diagrams, or independent evaluation.

    Codeshipcloudbees.com10 min
  19. 148

    CloudBees vs Harness: Why Migration Isn't the Fix

    The article argues that Harness’s “free migration” offer hides significant downstream costs (training, pipeline rebuilds, compliance recertification) and that even after migration you still lack unified governance across heterogeneous CI/CD tools. CloudBees positions its Unify control plane as a tool‑agnostic layer that adds visibility, continuous governance, AI‑driven test selection, and hybrid…

    Codeshipcloudbees.com5 min
  20. 149

    The 2026 State of Code Abundance Report: Exposing the Enterprise AI Readiness Gap

    A report highlights a significant gap between enterprise confidence in AI-generated code and operational reality, with 81% of leaders reporting increased production issues despite high readiness scores. This "code abundance" means code is generated faster than organizations can effectively test, govern, and manage it, leading to challenges in cost attribution and governance.

    Codeshipcloudbees.com5 min
  21. 150

    Merge Conflict: Everything You Need to Know

    This article explains what Git merge conflicts are, why they occur when merging different changes to the same file locations, and how they manifest differently in standard merges versus rebases. It provides a strategy for resolving rebase conflicts in feature branches before merging them into a main branch.

    Codeshipcloudbees.com5 min
devops posts and papers · proomt