InfoQOlimpiu Pop3 min readadvanced
Google Rewrites Critical C Dependencies to Rust Using AI and Differential Fuzzing
Summary
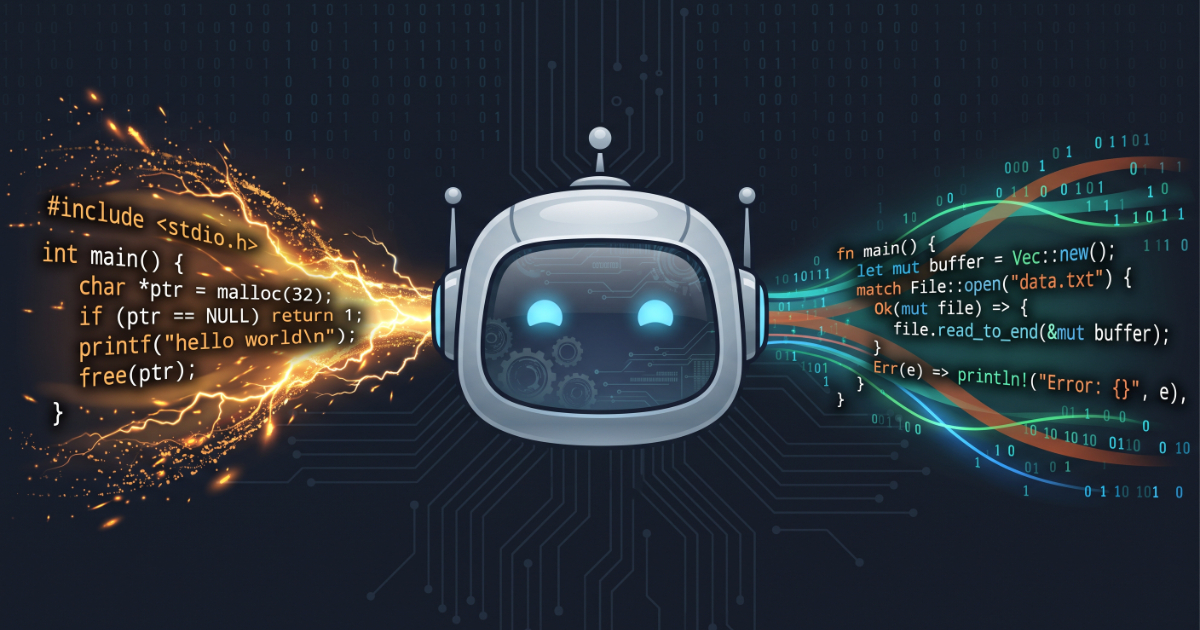
Google successfully used Gemini AI and differential fuzzing to rewrite giflib, a critical C dependency, into memory-safe Rust. This process created an ABI-compatible drop-in replacement, preempted a zero-day vulnerability, and improved p99 tail latency by enabling the removal of process isolation sandboxes.
- Gemini AI performed a single-shot C to Rust translation, retaining original symbols for ABI compatibility.
- Rigorous validation included mass-scale regression decoding (30M GIFs) and 6 days of differential fuzzing (200M iterations).
- The Rust rewrite preempted CVE-2026-26740 and allowed decommissioning OS sandboxes, improving p99 latency.
- FFI wrappers required human expertise to manage raw pointer semantics, ownership, and lifetime invariants.
Engineers facing legacy C/C++ security vulnerabilities and performance bottlenecks should consider this AI-assisted, fuzzer-validated migration path to memory-safe languages like Rust.
7/10