proomt

Search

Search posts, papers, and topics

security

RSS
  1. 121

    No, You're Not Behind. But the Stage 3 Governance Window Is Closing.

    A four‑stage model for adopting agentic AI in software delivery pipelines, warning that Stage 3 (bounded autonomous execution) is arriving faster than governance programs. The post explains the stages, required controls (scoped credentials, fail‑closed defaults, tamper‑evident logs), and uses the OpenClaw incident as a cautionary example.

    Codeshipcloudbees.com9 min
  2. 122

    webaudio fingerprinting on alibaba

    Firefox made WebAudio output deterministic in v118, collapsing most variance to three CPU‑dependent buckets (x86 without FMA, x86/x64 with FMA, ARM NEON). Telemetry shows 99.24% of users fall into these buckets; a long tail of 23 distinct values affects <0.1% of users. Ongoing bugs aim to merge the remaining buckets. Alibaba’s fingerprint script was extracted (two SHA‑256 hashes) and shown to be…

    Mozilla Automation Teamritter.vg3 min
  3. 123

    OpenClaw Is a Preview of Why Governance Matters More Than Ever

    Autonomous AI agents like OpenClaw are shifting software development from AI-assisted to AI-executed, capable of committing code and orchestrating deployments without human approval. This necessitates robust governance to manage increased risks in security, compliance, and accountability, as traditional DevOps assumptions no longer hold.

    Codeshipcloudbees.com6 min
  4. 124

    When should you replace a homegrown feature flag system?

    Homegrown feature flag implementations work for small teams but quickly lack ownership, auditability, and stakeholder access as they scale. When flag count, team size, incidents, or compliance audits make these gaps costly, switch to a purpose‑built feature management platform.

    Codeshipcloudbees.com5 min
  5. 125

    App Hardening: One Obfuscation Pipeline Across Every Port

    Codename One adds a cloud‑side hardening step that runs on the merged JAR before it is split into Android, iOS, JavaScript, and desktop binaries. It can rename symbols, encrypt string literals, and insert opaque‑predicate control‑flow guards at configurable levels (off → standard → aggressive → paranoid). The transforms are selective per platform to avoid breaking optimizers, and a mapping is kep…

    CodeName Onecodenameone.com6 min
  6. 127

    Auth0 Agent Gateway: The Identity Control Plane for Customer-Facing AI

    Auth0 Agent Gateway is a beta CIAM control plane that lets SaaS teams govern product‑native, customer‑facing AI agents. It adds organization‑aware identity, token‑exchange‑based credential delegation, real‑time policy checks, audit logging and a kill‑switch, aiming to prevent cross‑tenant data leaks and unauthorized tool use.

    Auth0auth0.com6 min
  7. 128

    6 Ways Traditional API Design Has Changed Forever

    API design is shifting from human‑centric, resource‑based REST toward machine‑friendly, capability‑oriented interfaces as AI agents become major consumers. This drives changes in rate limiting, just‑in‑time security, system‑wide reliability, and regulatory compliance.

    Nordic APIsnordicapis.com6 min
  8. 129

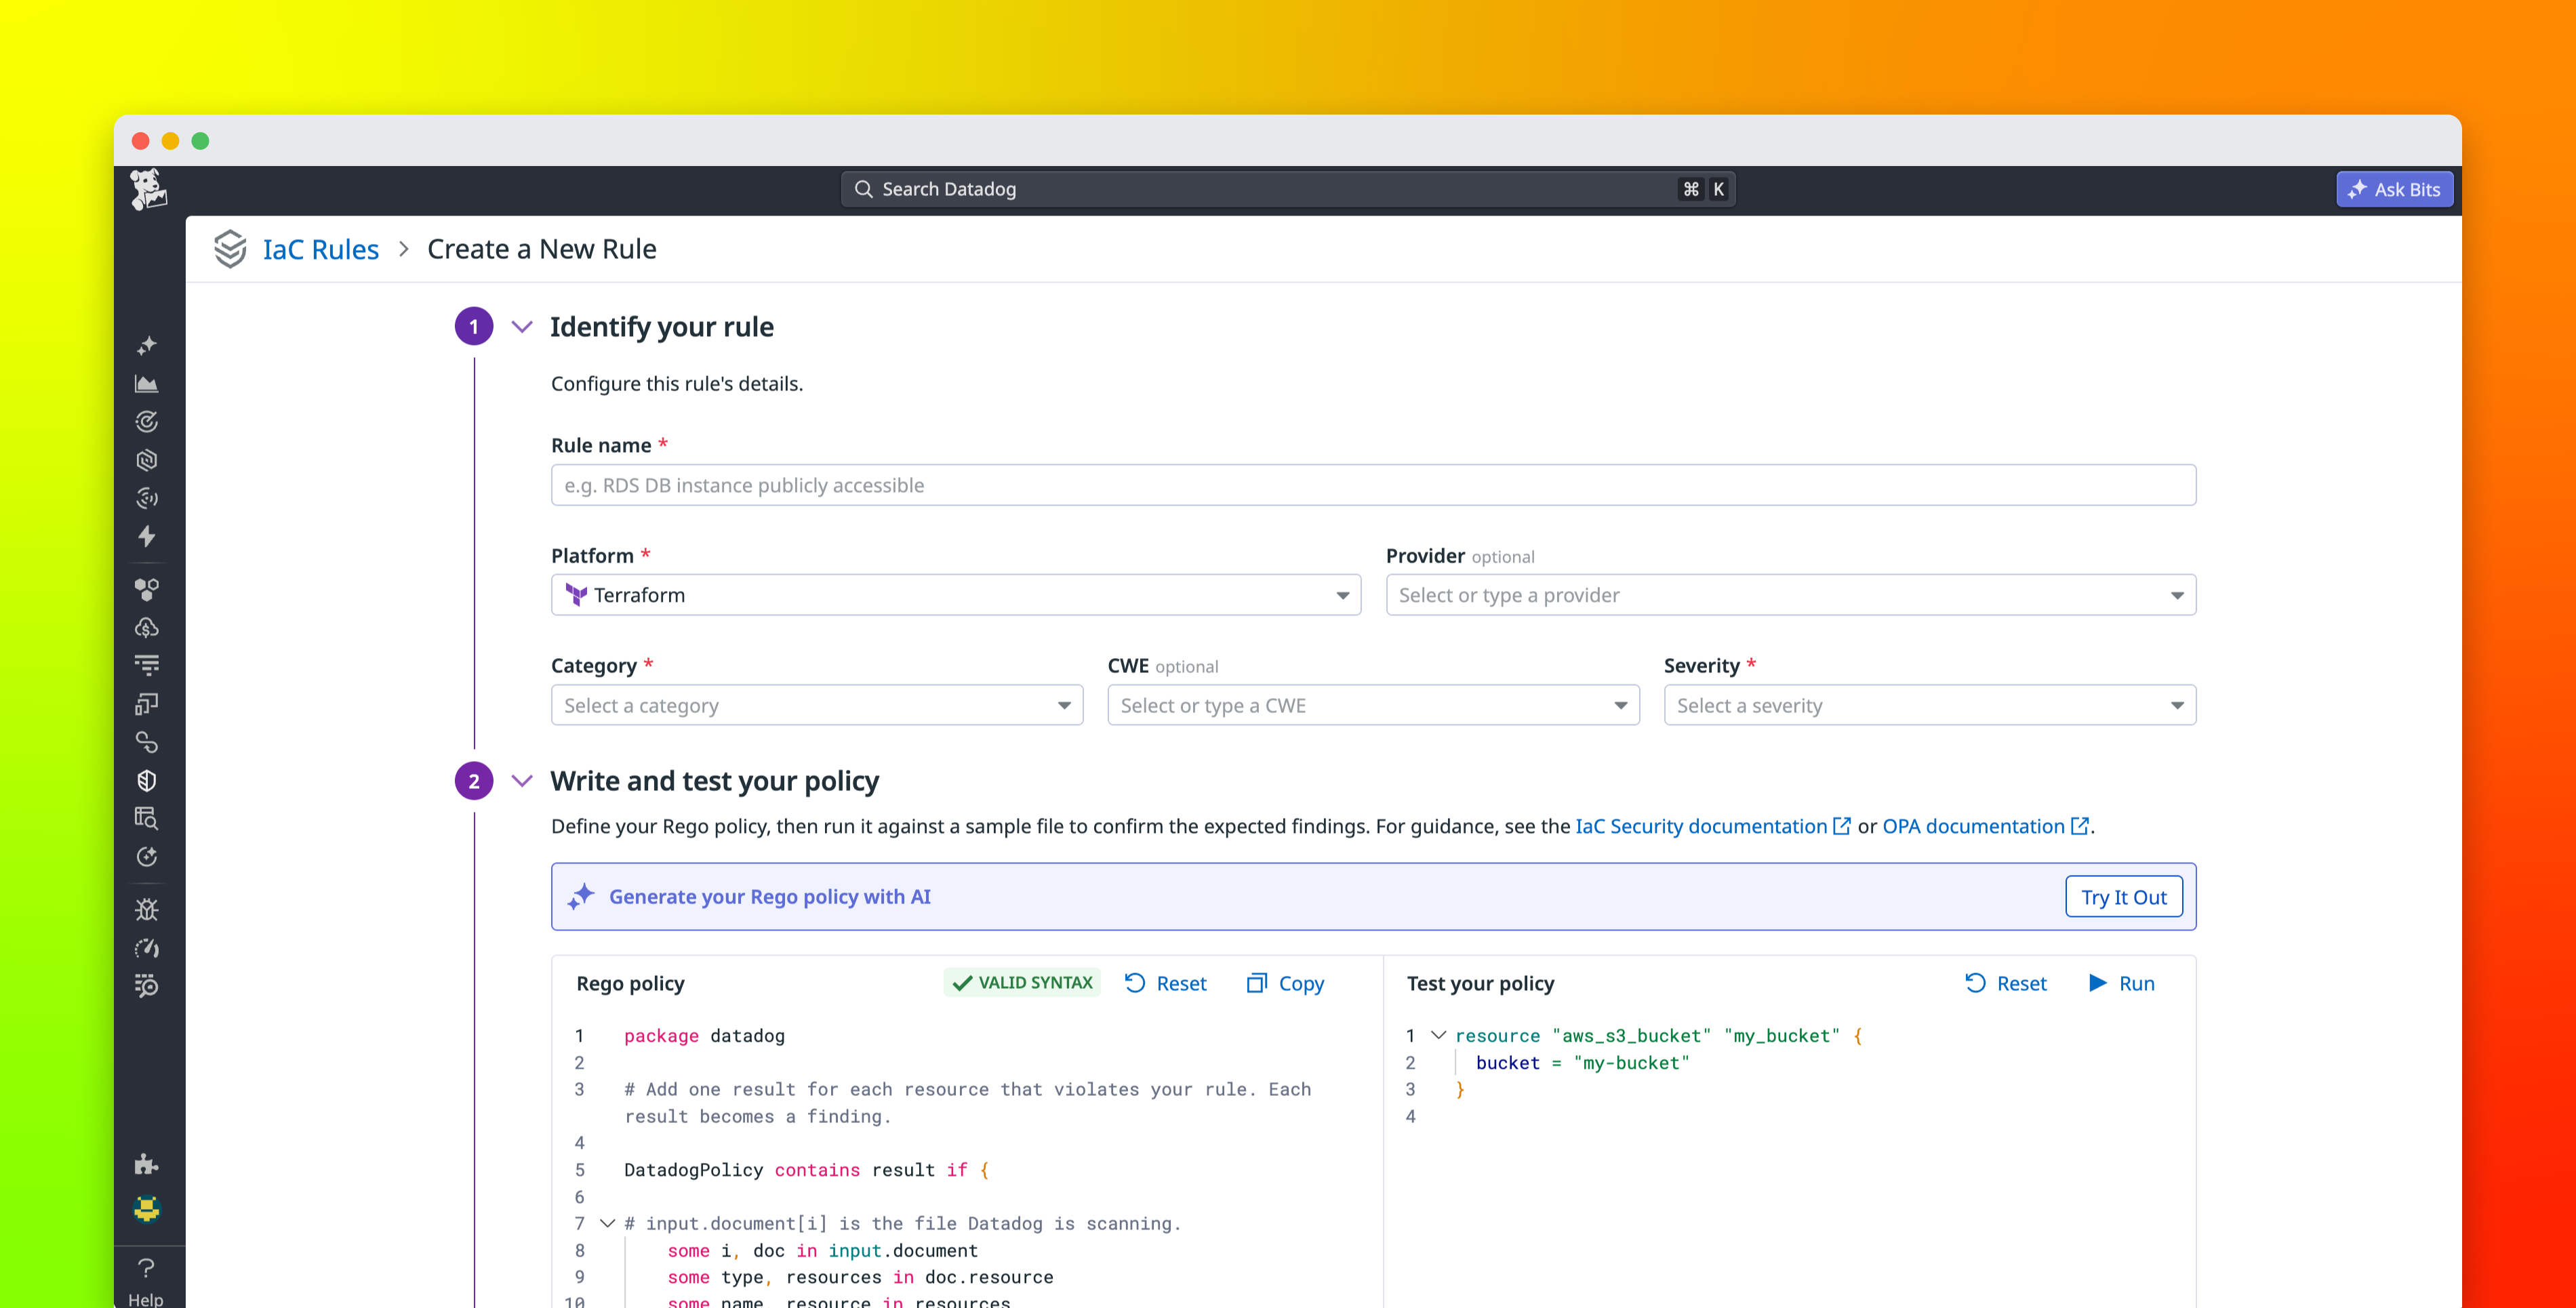
    Enforce custom rules in Datadog IaC Security scanning

    Datadog now lets you write organization‑specific IaC security checks as Rego policies that run alongside its built‑in rule set. You can author, test, version, and publish custom rules via the UI (or AI‑assisted generation), then see violations in PR comments, IDE extensions, or automation pipelines.

    Datadogdatadoghq.com5 min
  9. 130

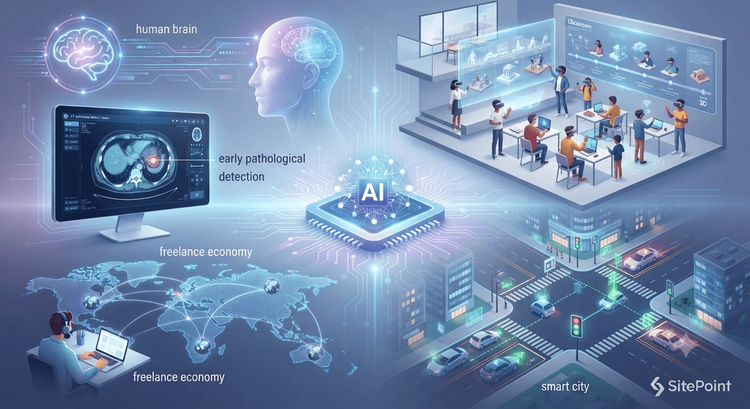
    Integrating AI Across Industries: A Developer’s Guide to Practical Frameworks

    The article surveys common AI integration patterns—high‑throughput streaming with Kafka/Kinesis, edge object detection on Jetson, CI/CD for full‑stack freelance apps, and security/bias safeguards—but offers only high‑level guidance. It outlines the technologies and best‑practice checkpoints developers should consider when building scalable, secure AI services.

    SitePointsitepoint.com1 min
  10. 131

    Laravel Vet: Review Composer Code Before It Installs

    Laravel Vet is a Composer plugin that intercepts installs/updates, shows the diff of each package, and lets you approve changes manually or via an LLM‑based coding agent. Trusted packages are recorded in a `vet.json` with a content hash, so future updates only prompt for new changes. The tool exits with an error on untrusted code, making it CI‑friendly, and works with any PHP project using Compos…

    Laravellaravel-news.com4 min
  11. 133

    Optimize Your Identity Flows with Auth0 Identity Conversion Suite

    Auth0 announced the early‑access Identity Conversion Suite, which adds two features—Anonymous Sessions (tracking a user before they log in via OAuth‑compatible tokens) and Experiment Center (feature‑flag‑driven A/B testing of auth flows). The post explains the intended use cases (guest checkout, secure anonymous API access, passwordless sign‑up, MFA sizing) but provides no implementation details,…

    Auth0auth0.com7 min
  12. 134

    Mila and Mozilla announce new initiative to build trustworthy open source AI for everyone, with Canadian government support

    Mozilla and Mila, backed by $5 M from Mozilla and $1 M from Hypertec plus Canadian government support, announce an open‑source AI foundation layer aimed at letting small organisations run private AI models. The post describes the high‑level vision (open standards + reference implementation) and a two‑year rollout plan, but provides no technical details, design rationale, or measurable results.

    Mozilla Automation Teammozilla.org5 min
  13. 135

    AWS Cannot Restore Data Held Only in Damaged Middle East Availability Zones

    AWS admitted it cannot recover data that was stored only in the damaged Availability Zones of its Middle East (UAE) and Bahrain regions after Iranian drone strikes. The outage highlights that AWS’s multi‑AZ guarantees only protect against localized failures, not regional destruction, and that customers must implement cross‑region replication to meet durability and data‑residency requirements.

    InfoQinfoq.com5 min
  14. 137

    What is CIAM in 2026 and why does it matter?

    CIAM in 2026 has moved from static login checks to a continuous trust layer that must handle AI agents, deep‑fake attacks, and zero‑friction authentication, requiring a split between an identity authority and a real‑time trust orchestration layer.

    Twiliotwilio.com9 min
  15. 138

    The Shadow Factory: Why Your CI/CD Sprawl is About to Move Faster Than You Can Think

    The article warns that unchecked CI/CD sprawl— orphaned pipelines, hard‑coded secrets, and permissive runners— creates a hidden attack surface, and that AI‑driven agents will amplify the problem. It recommends a governance layer with real‑time inventory, policy‑as‑code, and AI guardrails to bring the software factory under the same security rigor as production.

    Codeshipcloudbees.com3 min
  16. 140

    Introducing the DevOps Agent Kit

    The DevOps Agent Kit is an Apache‑2.0 open‑source starter kit that lets you plug an LLM‑based coding assistant into your existing CI/CD, security, and feature‑flag tooling via CloudBees Unify. It ships with seven read‑only example skills, enforces RBAC and audit trails, and normalises data from up to 63 tools so the agent can answer a single “are we good to ship?” question with verifiable evidenc…

    Codeshipcloudbees.com5 min
  17. 141

    Fine-Grained Access Control Now Available for All Heroku Customers

    Heroku replaces its static role model with per‑app fine‑grained permissions (view, deploy, operate, manage). The new model is exposed via the Dashboard, Heroku CLI (v11.10+), and Platform API, enabling teams to enforce least‑privilege, improve compliance, and automate access provisioning.

    Herokuheroku.com3 minrelease
  18. 142

    Give your eve agent a browser

    Vercel released the @agent-browser/eve extension, giving Eve agents full browser automation capabilities inside their sandbox. It adds installable tools for navigation, interaction, and screenshots, with domain allowlists and credential protection.

    Vercelvercel.com1 minrelease
  19. 143

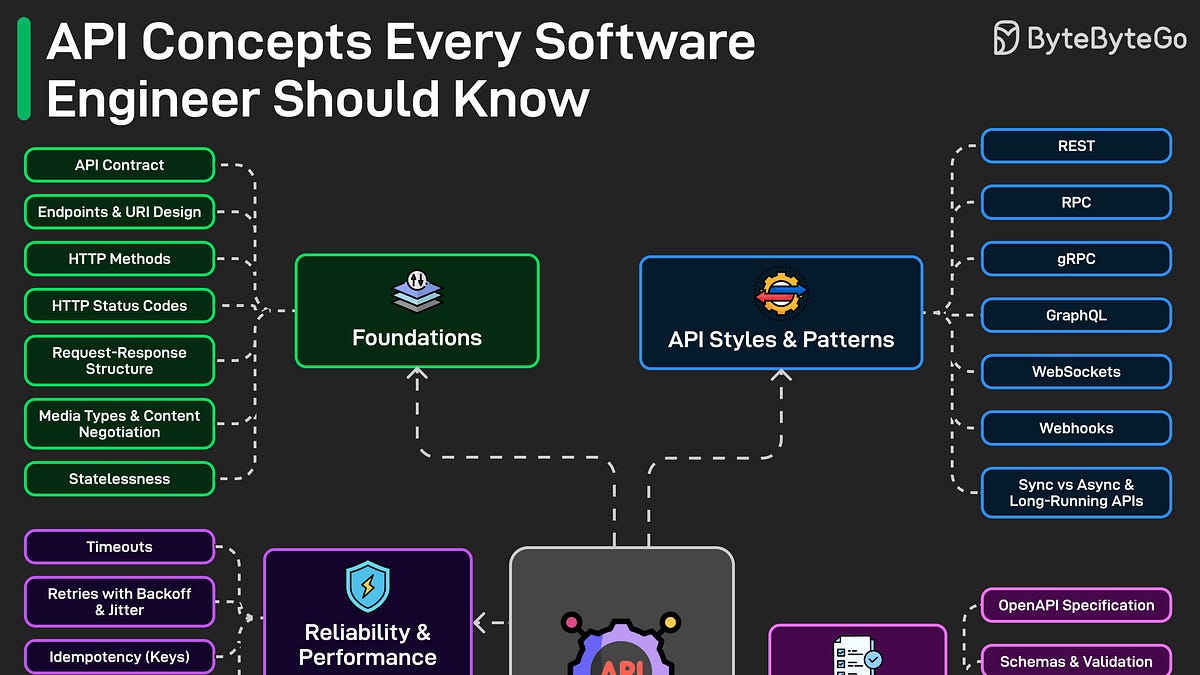
    EP226: API Concepts Every Software Engineer Should Know

    This article outlines essential API design considerations, covering HTTP fundamentals, architectural styles like REST and GraphQL, and critical aspects such as naming, versioning, security, and reliability. It serves as a high-level checklist for engineers designing or consuming APIs.

    ByteByteGobytebytego.com5 min
  20. 145

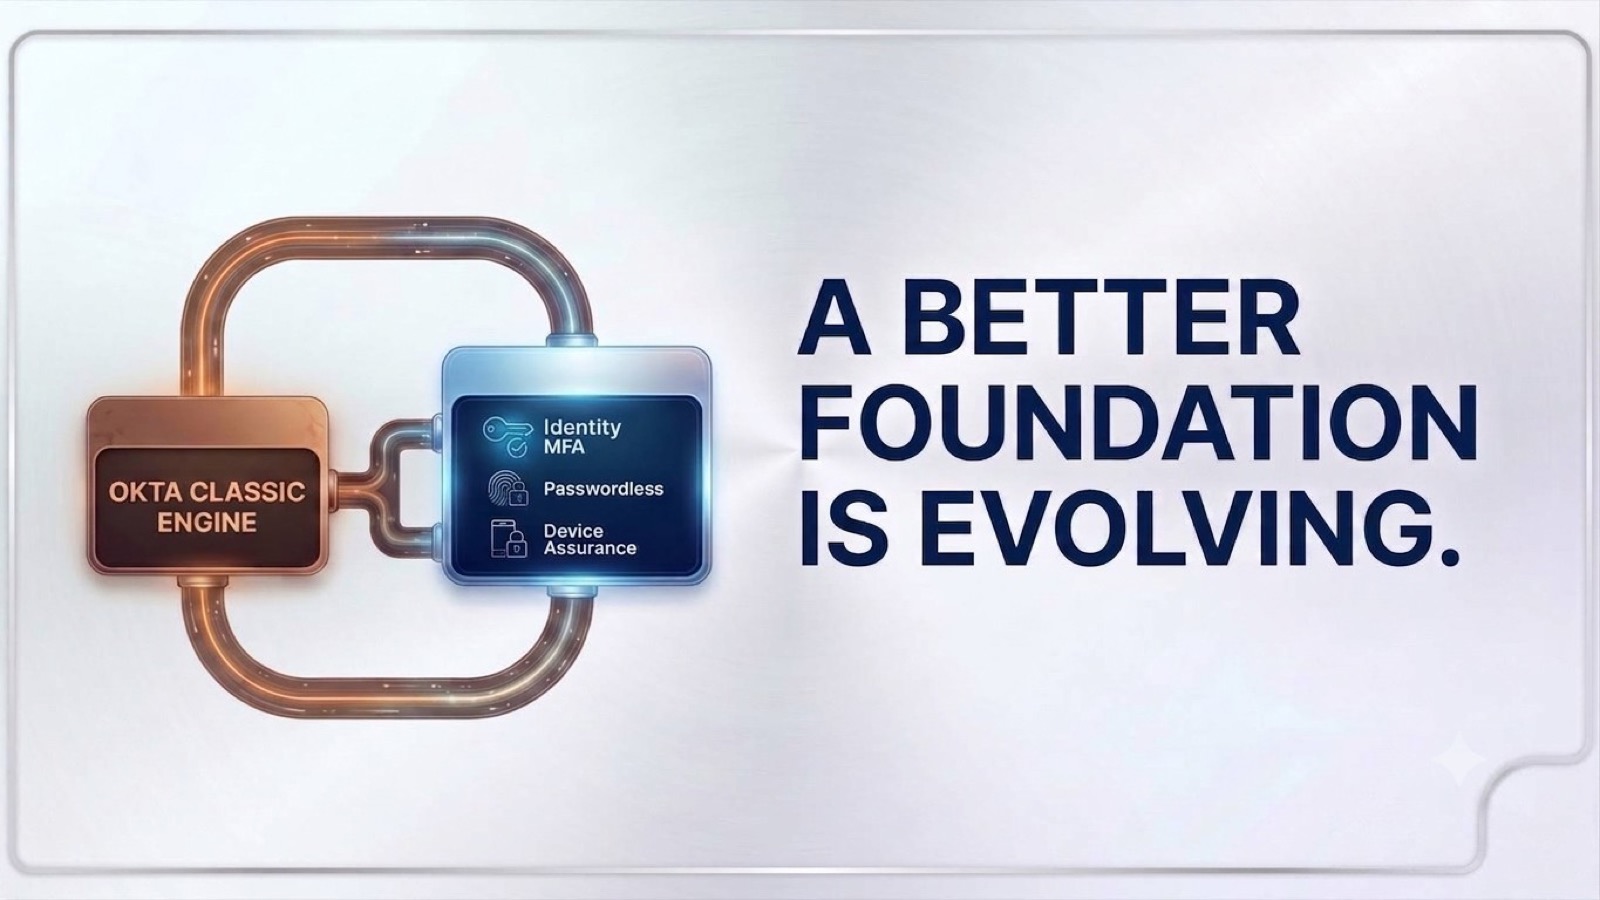
    Classic Engine Feature EOL: SSR, Desktop SSO, Device Trust

    Okta is ending support for Self-Service Registration, Desktop SSO (IWA), and Device Trust on its Classic Engine by March 5, 2027. Users must migrate to Okta Identity Engine to retain these capabilities and gain access to modern security features like passwordless authentication and device assurance.

    Oktaokta.com4 minrelease
  21. 146

    The only perfect Endpoint Prevention and Response (EPR) score in 2026 belongs to Elastic

    Elastic Security achieved a perfect 100% score in AV‑Comparatives’ 2026 Endpoint Prevention and Response (EPR) test, stopping all 50 attack scenarios at the prevention stage with zero false positives or workflow delays. The test measured active prevention, passive detection, operational accuracy, and workflow impact across 14 vendors. Elastic’s claim is backed by open‑source protection rules and…

    Elasticelastic.co5 min
  22. 148

    Every tool is green. Can you ship?

    A CloudBees blog post argues that existing CI, security, and QA tools don’t give release managers a complete view of AI‑generated code risk. It claims tool consolidation rarely helps and proposes a “control plane” (CloudBees Unify) that aggregates signals from multiple tools and adds AI‑driven test prioritization. The piece is largely promotional, with no concrete implementation details, metrics,…

    Codeshipcloudbees.com4 min
  23. 149

    What Continuous Security Is and What It Isn’t

    The article defines continuous security as an AI‑augmented, unified control plane that embeds security checks into CI/CD pipelines, contrasting it with fragmented tool sprawl that creates alert fatigue. It promotes CloudBees Unify as a solution that deduplicates findings, enforces policy‑as‑code, and automates audit evidence.

    Codeshipcloudbees.com4 min
  24. 150

    Introducing ElectricCommander 4.2

    ElectricCommander 4.2 adds a redesigned Resources UI, bulk agent install/upgrade, optional trusted SSL connections, zone‑based segmentation with gateways, new API commands, JSON transport, and a bundled standard license. The release is a typical product update with no deep technical analysis.

    Codeshipcloudbees.com3 minrelease